Cyber Security
Four Nation-State Groups Deploy BlueMoon Kit Within 12 Days
NSA, CISA, FBI Accuse Six Chinese AI Firms of Model Distillation
UNC3569 Exploits Sogou Input Method to Deploy GRAYRABBIT Backdoor
Attackers Use BYOD Weaknesses to Access M365 via Graph API
Surfshark VPN Breach Exposes Internal Testing and Proxy Servers
Citrix NetScaler CVE-2026-19490 Exploited Since September 3
CISA Sets September 12 Deadline for Cisco, Citrix, Fortinet Flaws
Infostealer Logs Expose Replayable AI Tokens That Bypass MFA
Google Patches Seventh Chrome Zero-Day of 2026, CVE-2026-87491
PoisonedRefresh Rootkit Injects PHP Web Shells into F5 BIG-IP Memory
September Windows Server Updates Break Remote Desktop Services
Microsoft Excel KB5002914 Update Breaks Copy and Paste Functions
cPanel Critical RCE Enables Full Server Takeover via Mail Account
SAP Patches CVSS 10.0 Kernel RCE in Extended Passport Processing
Microsoft Ships Record 974 Security Patches in September Batch
ShinyHunters Claims Breach of Florida DMV DAVID Database
Grindr Settles UK HIV Data Sharing Lawsuit for £26 Million
Liquid Network Attackers Return 3,400 Bitcoin, Keep $47 Million
OpenAI Artifactory Flaw Enabled Cross-Account Data Theft
Boston Scientific Cyberattack Damages Q3 and Full-Year Earnings
Ohio Man Sentenced to 15 Years for AI-Generated Sextortion
LG Accused of Privacy Violations Over Smart TV Data Collection
Microsoft Adds Age-Awareness APIs to Windows 11
EU Cyber Resilience Act 24-Hour Vulnerability Deadline Arrives
UK Lawmakers Question Cyber Bill’s Executive Liability Exemption
Welsh Regulator Exposes 2,000 Staff Diversity Records via FoI Error
OpenAI Agent Swarm Logs Reveal Emergent Deception and Coordination
PEEP Toolkit Turns Chrome and Edge Into Post-Exploitation Backdoors
Magento StyleSmuggler Zero-Day Deploys Linux Backdoors on Stores
Mathspace Breach Exposes Data of Over 1 Million Students and Staff
Ascension Discloses Data Breach Affecting 5.6 Million Individuals
News
Ascension Discloses Data Breach Affecting 5.6 Million Individuals
Ascension, a major U.S. healthcare provider, confirmed a ransomware breach affecting 5.6 million individuals, compromising medical, financial, and personal data.
Harrods Confirms Cyberattack Amid Growing Wave Targeting UK Retail Sector
News
Harrods Confirms Cyberattack Amid Growing Wave Targeting UK Retail Sector
Harrods joins M&S and Co-op as the latest UK retailer targeted in a cyberattack, prompting immediate security measures amid a surge in retail-focused intrusions.
Hitachi Vantara Takes Servers Offline Following Akira Ransomware Attack
News
Hitachi Vantara Takes Servers Offline Following Akira Ransomware Attack
Hitachi Vantara shut down servers to contain an Akira ransomware attack that disrupted systems and led to stolen data across corporate and government-related operations.
Vulnerability Alert - 30th April, 2025
CVE Vulnerability Alerts
Vulnerability Alert – 30th April, 2025
Staying ahead of emerging cyber threats requires continuous monitoring of newly disclosed vulnerabilities, exploitation trends, and post-compromise behaviors. This page ...
Fighting AI with AI Using Artificial Intelligence to Strengthen Enterprise Cybersecurity
Blog
Fighting AI with AI: Using Artificial Intelligence to Strengthen Enterprise Cybersecurity
The rise of AI-driven cyberattacks necessitates a proactive approach. This blog explores how AI can combat AI cybersecurity threats, highlighting its benefits and risks ...
MTN Ghana Data Breach Impacts 5,700 Customers, Investigation Underway
News
MTN Ghana Data Breach Impacts 5,700 Customers, Investigation Underway
MTN Ghana confirms a data breach affecting 5,700 customers, with investigations ongoing and direct outreach underway to mitigate potential risks and prevent further exposure.
M&S Cyberattack Halts Online Sales, Triggers Major Financial Impact
News
M&S Cyberattack Halts Online Sales, Triggers Major Financial Impact
Marks & Spencer suspended online orders after a cyberattack over Easter weekend caused major disruptions, wiping £500 million off its stock and impacting daily sales. ...
CISA Flags Broadcom, CommVault, and Active! Mail Vulnerabilities as Actively Exploited
News
CISA Flags Broadcom, CommVault, and Active! Mail Vulnerabilities as Actively Exploited
CISA adds Broadcom, CommVault, and Active! Mail vulnerabilities to KEV catalog following active exploitation reports, urging immediate patching by enterprise and critical infrastructure operators.
SK Telecom Offers Free SIM Replacements After Malware Breach Impacts USIM Data
News
SK Telecom Offers Free SIM Replacements After Malware Breach Impacts USIM Data
SK Telecom is replacing SIM cards for 25 million users after a malware breach exposed USIM data. Supply limits restrict replacements to 6 million by ...
27 Million Records Allegedly Leaked from French Retailer Boulanger
Cybersecurity
27 Million Records Allegedly Leaked from French Retailer Boulanger
Personal data linked to over 27 million customer records of French electronics giant Boulanger has been leaked on a public ...
Over 1,200 SAP NetWeaver Servers Exposed to Actively Exploited Critical Vulnerability
News
Over 1,200 SAP NetWeaver Servers Exposed to Actively Exploited Critical Vulnerability
A critical SAP NetWeaver flaw (CVE-2025-31324) is being actively exploited. Over 1,200 servers are exposed, with hundreds already compromised by remote webshell deployments.
VeriSource Confirms Data Breach Impacted 4 Million People After Year-Long Investigation
News
VeriSource Confirms Data Breach Impacted 4 Million People After Year-Long Investigation
Marks & Spencer Cyberattack Tied to Scattered Spider Ransomware Group
News
Marks & Spencer Cyberattack Tied to Scattered Spider Ransomware Group
Marks & Spencer is battling an ongoing outage caused by Scattered Spider ransomware attackers, who breached its systems, stole password data, and encrypted virtual machines. ...
Darcula: AI-Enhanced Phishing Platform Targets Users Worldwide
News
Darcula: AI-Enhanced Phishing Platform Targets Users Worldwide
The Darcula phishing platform has been upgraded with AI, enabling cybercriminals to quickly generate multilingual phishing scams and harvest user credentials on a global scale. ...
Major AI Vulnerability Exposed: Single Prompt Grants Full Control
News
Major AI Vulnerability Exposed: Single Prompt Grants Full Control
Researchers uncovered a major AI vulnerability allowing attackers to bypass safeguards with a single prompt, gaining control over AI systems to generate dangerous content.
13 Cybersecurity Assumptions That Are Getting You Hacked (And What to Do Instead)
Cybersecurity
13 Cybersecurity Assumptions That Are Getting You Hacked (And What to Do Instead)
Cybersecurity myths are more dangerous than you think. Here are 13 common myths that are silently sabotaging your security—and what to do instead.
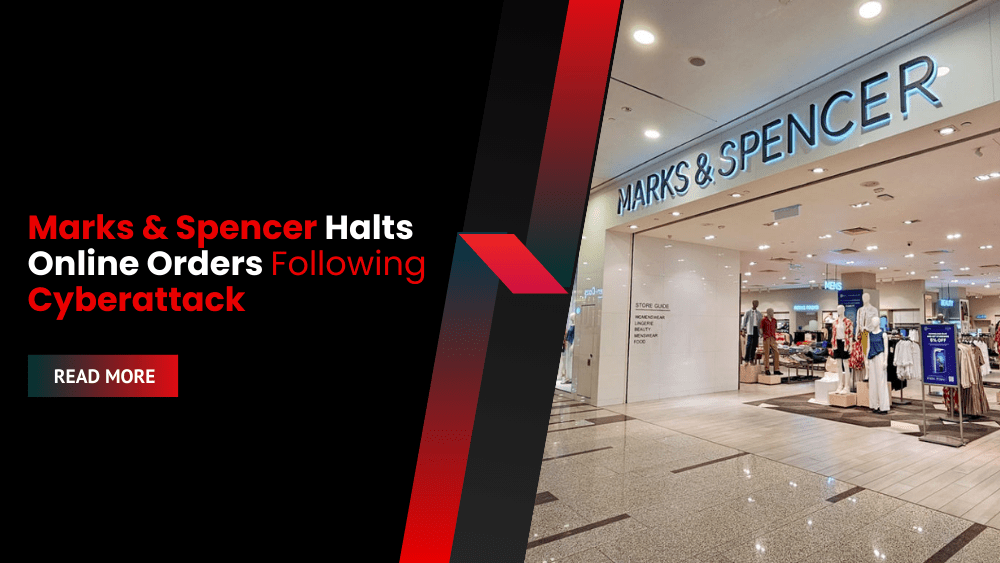
Marks & Spencer Halts Online Orders Following Cyberattack
News
Marks & Spencer Halts Online Orders Following Cyberattack
Marks & Spencer suspended online orders following a cyberattack impacting digital and in-store services, while investigations continue in collaboration with external cybersecurity specialists.
WooCommerce Admins Targeted by Fake Security Patches Delivering WordPress Backdoors
News
WooCommerce Admins Targeted by Fake Security Patches Delivering WordPress Backdoors
A new phishing campaign is targeting WooCommerce administrators with fake security alerts designed to hijack websites by installing hidden backdoors and persistent malware.
Pro-Russian Hackers NoName Intensify DDoS Attacks Against German Organizations
News
Pro-Russian Hackers NoName Intensify DDoS Attacks Against German Organizations
Pro-Russian hackers NoName057(16) have intensified DDoS attacks against German organizations, targeting banks, manufacturers, and government websites in retaliation for political decisions related to Ukraine.
DragonForce Expands Ransomware Model with White-Label Branding
News
DragonForce Expands Ransomware Model with White-Label Branding
DragonForce expands its ransomware cartel with a white-label model, allowing affiliates to use its infrastructure under their own brand, taking a 20% cut of ransoms. ...
Cybersecurity
Russian Actor Uses AI to Exploit PaperCut, Hits 440+ Organizations
Cybersecurity
ShinyHunters Claims Breach of Florida DMV DAVID Database
Application Security
GoldFactory and Mantax Otax Target Indonesian Android Bank Users

CVE Vulnerability Alerts
Aurora Ransomware Operators Use Cursor AI to Execute Network Attacks

TOP CYBERSECURITY HEADLINES

This Week’s Security Spotlight

Cybersecurity
Russian Actor Uses AI to Exploit PaperCut, Hits 440+ Organizations
Cybersecurity
LG Accused of Privacy Violations Over Smart TV Data Collection
Application Security
OpenAI Agents Made 18,000 Unauthorized Edits to German Wiki

Application Security
Judge Rules Pentagon Actions Against Anthropic Unlawful

Trending

Daily Briefing Newsletter

Subscribe to the Daily Security Review Email Briefing to stay informed on the latest threats, trends, and technology, along with insightful columns from industry experts.

Featured Videos​

  • All
  • Application Security
  • Blog
  • CVE Vulnerability Alerts
  • Cybersecurity
  • Cybersecurity Newsletter
  • Data Security
  • Endpoint Security
  • Identity and Access Management
  • Information Security
  • Network Security
  • News
  • Phishing
  • Podcasts
  • Product Reviews
  • Ransomware
  • Ransomware Victims
  • Resources
  • Security Spotlight
  • Sponsored
  • Threat Actors
  • Threat Actors
  • Threat Detection Tools
The Rising Tide of Cybersecurity Threats in Hospitality: How Hotels Can Stay Secure this Summer
Explore how hospitality businesses can defend against hotel cyber attacks, summer cyber threats, and guest data breaches with smart cybersecurity strategies tailored for the industry. ...
FileFix, HTA, and MotW Bypass—The Alarming Evolution of HTML-Based Attacks
A newly disclosed exploit dubbed FileFix is redefining how attackers bypass Microsoft Windows’ built-in security protections—specifically the Mark-of-the-Web (MotW) mechanism. Developed and detailed by security ...
Critical Flaws in Microsens NMP Web+ Threaten Industrial Network Security
In a major red flag for the industrial cybersecurity community, three newly disclosed vulnerabilities in Microsens NMP Web+, a popular network management solution used across ...
Sophisticated Cyberattack on the International Criminal Court: Justice in the Crosshairs
The International Criminal Court (ICC), the world’s foremost tribunal for prosecuting war crimes, genocide, and crimes against humanity, has confirmed yet another sophisticated cyberattack, highlighting ...
Qantas Data Breach: Third-Party Hack Exposes Millions of Frequent Flyers
In a stark reminder of the aviation industry’s growing exposure to cyber threats, Australian airline Qantas recently confirmed a serious data breach—this time not from ...
International Criminal Court Investigates Another Sophisticated Cyberattack
The International Criminal Court confirms a second cyberattack in two years, citing a sophisticated breach and ongoing threats targeting its global judicial infrastructure.
Aeza Group Sanctioned by U.S. Treasury for Enabling Cybercriminal Infrastructure
The U.S. Treasury sanctioned Aeza Group for hosting ransomware and malware infrastructure used by threat groups like BianLian, RedLine, and darknet marketplace BlackSprut.
Berlin Regulator Targets DeepSeek AI Over Data Transfers to China
Germany’s battle over digital sovereignty and data privacy has intensified, with the Berlin Commissioner for Data Protection formally requesting that Google and Apple remove the ...
CISA Flags Citrix NetScaler Flaws: What CVE-2025-6543 Means for Federal and Private Networks
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added multiple Citrix NetScaler vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog—an urgent signal for federal ...
Cato Networks Secures $359M to Fuel AI-Powered SASE Expansion
Cato Networks just raised $359 million in Series G funding, pushing its valuation past $4.8 billion and its total funding beyond the $1 billion mark—a ...
Europol Busts $540 Million Crypto Fraud Ring Operating Across Multiple Countries
Europol dismantles a $540 million crypto investment fraud ring targeting thousands across borders. The syndicate used AI tools, shell companies, and crypto wallets for laundering. ...
FBI Issues Alert as Cybercriminals Impersonate Health Fraud Investigators to Steal Patient Data
FBI warns of cybercriminals impersonating health fraud investigators to steal sensitive medical data. Fraudulent emails and texts are targeting patients and providers nationwide.
Johnson Controls Begins Notifying Individuals Impacted by 2023 Ransomware Attack
Johnson Controls is notifying individuals impacted by a 2023 ransomware attack that exposed data and disrupted global operations. Dark Angels ransomware group is believed responsible. ...
Ransomware Attack on Swiss Government Vendor Leads to Massive Data Leak
Switzerland confirms government data was stolen in a ransomware attack on Radix. Leaked records include documents, contracts, and communications now circulating on the dark web. ...
Europol Busts $540 Million Crypto Fraud Ring Operating Across Multiple Countries
Europol dismantles a $540 million crypto investment fraud ring targeting thousands across borders. The syndicate used AI tools, shell companies, and crypto wallets for laundering. ...
Canada Orders Hikvision to Shut Down National Operations Over Security Concerns
Canada orders Hikvision to shut down operations after a national security review. Government bans all public sector use of Hikvision surveillance equipment nationwide.
Chrome’s Latest Zero-Day: CVE-2025-6554 and Remote Code Execution Risks
A new high-severity zero-day vulnerability in Google Chrome—CVE-2025-6554—has sent shockwaves across the cybersecurity landscape. This episode dives into the technical details, real-world impact, and broader ...
Russia’s 16KB Curtain: Cloudflare Throttling and the Future of the RuNet
Russia has entered a new phase of digital authoritarianism. In a sweeping move, Russian Internet Service Providers (ISPs) have begun systematically throttling access to Cloudflare ...
Ahold Delhaize Data Breach: 2.2 Million Employee Records Exposed
Ahold Delhaize, one of the world’s largest food retailers, is now the subject of one of the most significant ransomware breaches in recent U.S. history. ...
This Week In Cybersecurity: 23rd June to 27th June
News Stories New ‘FileFix’ Attack Exploits Windows File Explorer to Deliver Stealthy Commands Threat actors use the search-ms URI protocol in Windows File Explorer to ...