Cyber Security
Arista Patches Exploited VeloCloud Orchestrator Zero-Day
eMudhra Exits TLS Business as Chrome and Oracle Distrust Its Keys
Okta Patches Four Access Gateway Flaws Including CVSS 9.1 Bug
ZDI Posts Unpatched Linux KSMBD RCE Flaws to Public Mailing Lists
CISA Warns of Nine Kiloview E3 Encoder Flaws, Two at CVSS 9.9
HPE Patches 72 Aruba AOS-8 and AOS-10 Flaws, Eight at CVSS 10.0
Railway Says Intruder May Have Decrypted Customer Secrets
INTERPOL Operation Serengeti III Nets 1,462 Arrests in Africa
Node.js Security Releases Fix Brotli Out-of-Bounds Write Flaw
Onamae Desktop Cloud Hacked; Malware on Up to 26,739 Servers
Columbia, South Carolina Takes Systems Offline After Cyberattack
FoxIO QPACK Flaws Crash HTTP/3 Servers via 4,000x Amplification
LiteLLM 1.107.0 Backdoored in PyPI Supply Chain Attack
Microsoft Ties ConnectWise Backup Attack to China-Aligned Storm-0940
PHP Ships Emergency Patches for PHP2Shell as Exploitation Begins
Signal RingRTC Flaw CVE-2026-113380 Can Keep Mic and Camera On
Exposed Servers Reveal INC and Gentlemen Ransomware AI Operations
WhiteArmour Claims Breach of Disney Staff Directory
Chrome 156 Patches 353 Security Flaws, Six Rated Critical
PHP Warns of Two Critical RCE Flaws as Embargoed Details Leak
DHS Orders Federal Civilian Agencies to Remove DeepSeek Products
Feds Suspect Ransom Negotiator Helped Run ShinyHunters Leak Site
23andMe Successor Settles With California for $6M Over Breach
ICO Reprimands Welsh Bodies After ‘Password1’ Account Breach
Mozilla, Google, Apple Block Eight Weak eMudhra CA Keys
Hacker Claims NBCUniversal Production and Tax-Credit Data Theft
Hijacked Account Plants Stealer in Five OVHcloud CLI Releases
CISA, FBI Say SafePay Ransomware Has Hit 600+ Organizations
Public Exploit Released for Critical FortiSIEM Flaw CVE-2026-106173
State Bank of India Confirms Data Leak of 3,897 Customer Records
OneClik Campaign Exploits Microsoft ClickOnce and AWS to Breach Energy and Industrial Networks
News
OneClik Campaign Exploits Microsoft ClickOnce and AWS to Breach Energy and Industrial Networks
A stealthy malware campaign abuses Microsoft ClickOnce and AWS services to deploy Golang-based RunnerBeacon backdoors targeting energy and industrial organizations with advanced evasion techniques.
Columbia University Struggles to Restore Services Following Suspected Cyberattack
News
Columbia University Struggles to Restore Services Following Suspected Cyberattack
Columbia University is working to restore critical systems following a suspected cyberattack that has caused widespread outages, impacting thousands of students and faculty.
CISA Confirms Active Exploitation of Critical AMI MegaRAC BMC Vulnerability Enabling Remote Server Hijack
News
CISA Confirms Active Exploitation of Critical AMI MegaRAC BMC Vulnerability Enabling Remote Server Hijack
CISA confirms that a critical vulnerability in AMI MegaRAC BMC firmware is being exploited to hijack servers remotely, prompting urgent patching across government and enterprise ...
Hacker 'IntelBroker' Indicted in $25M Global Data Theft Campaign
News
Hacker ‘IntelBroker’ Indicted in $25M Global Data Theft Campaign
British hacker ‘IntelBroker’ charged by U.S. authorities for stealing and selling sensitive data worldwide, causing $25 million in damage to governments and global enterprises.
French Authorities Arrest BreachForums v2 Operators Behind Global Data Theft Campaigns
News
French Authorities Arrest BreachForums v2 Operators Behind Global Data Theft Campaigns
French police arrest BreachForums v2 operators, including ShinyHunters and IntelBroker, tied to major global and national data breaches affecting millions of users and enterprises.
Scattered Spider: What You Know About It and What You Don’t
Blog
Scattered Spider: The Threat You Think You Know
Scattered Spider isn’t a single group but a sprawling web of identity-based attackers exploiting help desks, MFA gaps, and cloud admin tools to breach enterprises. ...
New FileFix Attack Exploits Windows File Explorer to Deliver Stealthy Commands
News
New FileFix Attack Exploits Windows File Explorer to Deliver Stealthy Commands
A researcher has revealed a new FileFix attack that abuses Windows File Explorer’s address bar to stealthily execute commands, expanding on previous ClickFix phishing techniques. ...
Trojanized SonicWall NetExtender Client Targets VPN Credentials via Spoofed Sites
News
Trojanized SonicWall NetExtender Client Targets VPN Credentials via Spoofed Sites
SonicWall and Microsoft have discovered a trojanized version of the NetExtender VPN client being distributed via spoofed websites, stealing remote access credentials from unsuspecting users. ...
New Spear Phishing Campaign Targets Financial Executives Using Legitimate Remote Access Tools
News
New Spear Phishing Campaign Targets Financial Executives Using Legitimate Remote Access Tools
A sophisticated spear phishing campaign is targeting CFOs and finance leaders worldwide, using legitimate tools like NetBird and OpenSSH to quietly breach enterprise networks.
Two Healthcare Data Breaches Expose Over 220,000 Records at Mainline Health and Select Medical
News
Two Healthcare Data Breaches Expose Over 220,000 Records at Mainline Health and Select Medical
Mainline Health and Select Medical Holdings have disclosed separate data breaches impacting more than 220,000 individuals, with ransomware and third-party compromise behind the incidents.
UK Government Warns of £1.6 Million in Ticket Scams Ahead of Glastonbury Festival
News
UK Government Warns of £1.6 Million in Ticket Scams Ahead of Glastonbury Festival
Concertgoers in the UK have lost over £1.6 million to ticket fraud in 2024, prompting urgent warnings from the government as festival season begins.
170K-Record Database Exposes Unencrypted PII from Real Estate Sector
News
170K-Record Database Exposes Unencrypted PII from Real Estate Sector
A misconfigured database tied to a U.S. real estate firm exposed 170,000 records of sensitive personal and internal data, including Social Security numbers and employment ...
Anubis Ransomware: A Destructive, Cross-Platform Threat
Resources
Anubis Ransomware: A Destructive, Cross-Platform Threat
Anubis ransomware combines encryption and file-wiping capabilities, targeting Windows, Linux, and NAS systems with stealthy command-line execution and affiliate-driven campaigns across multiple industries.
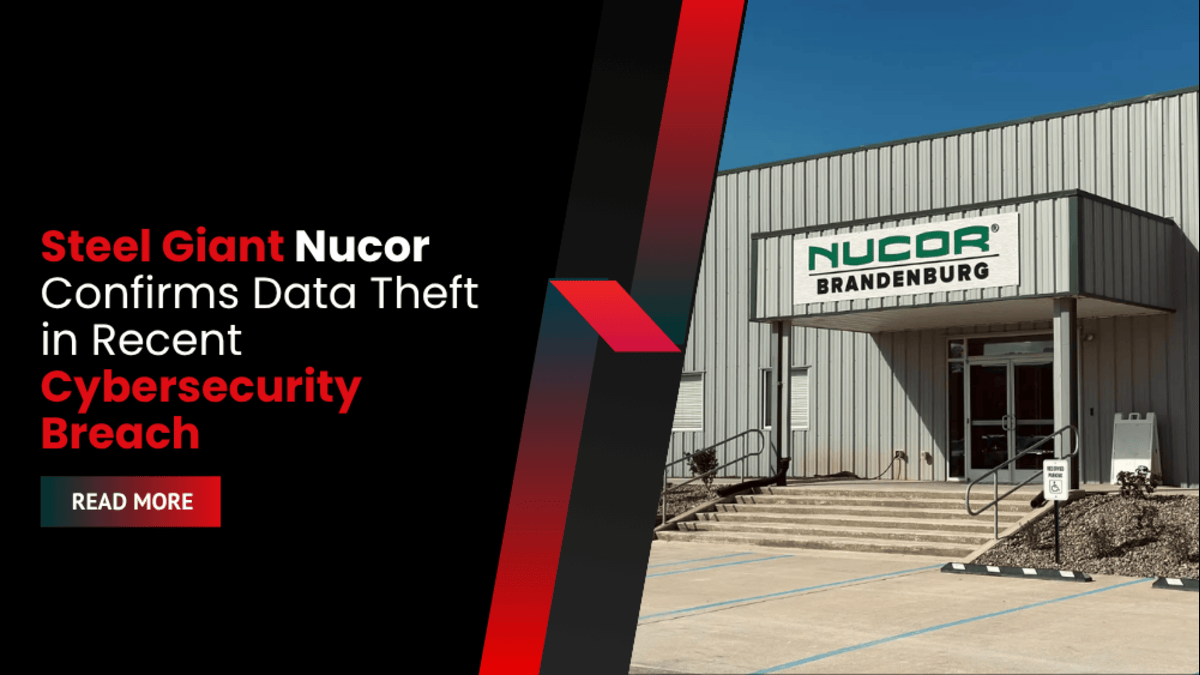
Steel Giant Nucor Confirms Data Theft in Recent Cybersecurity Breach
News
Steel Giant Nucor Confirms Data Theft in Recent Cybersecurity Breach
Nucor, North America’s largest steel producer, has confirmed data theft following a cybersecurity breach that temporarily disrupted operations and forced system shutdowns.
Chinese APT Group ‘Salt Typhoon’ Breaches Canadian Telecom Firm Using Cisco IOS XE Vulnerability
News
Chinese APT Group ‘Salt Typhoon’ Breaches Canadian Telecom Firm Using Cisco IOS XE Vulnerability
Canada confirms a state-sponsored breach in its telecom sector, where Salt Typhoon exploited an unpatched Cisco vulnerability to compromise devices and reroute sensitive network traffic. ...
Russia-Linked Hackers Deploy Sophisticated Social Engineering Attack and Evade MFA
News
Russia-Linked Hackers Deploy Sophisticated Social Engineering Attack and Evade MFA
Russian state-sponsored hackers targeted a critic of the Kremlin using a novel social engineering tactic that tricked the victim into bypassing multi-factor authentication protections.
16 Billion Passwords Exposed in Record-Breaking Breach: A Deep Dive into the Data Leak That Affects Everyone
News
16 Billion Passwords Exposed in Record-Breaking Breach: A Deep Dive into the Data Leak That Affects Everyone
A massive breach has exposed 16 billion login credentials, potentially affecting services like Facebook, Google, and Apple. This fresh infostealer data opens the door to ...
APT28 Hackers Use Signal to Target Ukraine with New Malware Families BeardShell and SlimAgent
News
APT28 Hackers Use Signal to Target Ukraine with New Malware Families BeardShell and SlimAgent
Russian threat group APT28 is using Signal messages to deliver new malware—BeardShell and SlimAgent—targeting Ukrainian government entities through sophisticated phishing and loader tactics.
Anubis Ransomware Gang Claims 64GB Disneyland Paris Leak in Alleged Construction Data Breach
News
Anubis Ransomware Gang Claims 64GB Disneyland Paris Leak in Alleged Construction Data Breach
Anubis ransomware group claims to hold 64GB of Disneyland Paris data, including engineering plans and behind-the-scenes content, though the source and sensitivity remain unclear.
McLaren Health Care Data Breach Exposes Personal Information of 743,000 Individuals
News
McLaren Health Care Data Breach Exposes Personal Information of 743,000 Individuals
McLaren Health Care has suffered a major data breach, exposing sensitive personal and medical data of 743,000 individuals, following a history of ransomware incidents.

Cybersecurity
Capcom ID Breach Exposes 11.77 Million Email Addresses
Cybersecurity
Capcom ID Breach Exposes 11.77 Million Email Addresses

Cybersecurity
Exposed Servers Reveal INC and Gentlemen Ransomware AI Operations
Cybersecurity
CISA, FBI Say SafePay Ransomware Has Hit 600+ Organizations

TOP CYBERSECURITY HEADLINES

This Week’s Security Spotlight

Application Security
GitLab Patches CVSS 10.0 Unauthenticated RCE Flaw CVE-2026-110264
CVE Vulnerability Alerts
Okta Patches Four Access Gateway Flaws Including CVSS 9.1 Bug

Cybersecurity
Columbia, South Carolina Takes Systems Offline After Cyberattack
Application Security
PHP Ships Emergency Patches for PHP2Shell as Exploitation Begins

Trending

Daily Briefing Newsletter

Subscribe to the Daily Security Review Email Briefing to stay informed on the latest threats, trends, and technology, along with insightful columns from industry experts.

Featured Videos​

  • All
  • Application Security
  • Blog
  • CVE Vulnerability Alerts
  • Cybersecurity
  • Cybersecurity Newsletter
  • Data Security
  • Endpoint Security
  • Identity and Access Management
  • Information Security
  • Network Security
  • News
  • Phishing
  • Podcasts
  • Product Reviews
  • Ransomware
  • Ransomware Victims
  • Resources
  • Security Spotlight
  • Sponsored
  • Threat Actors
  • Threat Actors
  • Threat Detection Tools
New Linux Backdoor “Plague” Evades Detection for Months
A stealthy Linux backdoor named Plague has evaded antivirus detection for months, exploiting PAM authentication modules to provide attackers with persistent SSH access and near-total ...
From Google to LVMH: ShinyHunters’ Salesforce Breaches Spark Global Ransom Crisis
A new wave of cyber extortion is sweeping across global enterprises, and the battlefield is Salesforce CRM. The notorious **ShinyHunters group—tracked internally by Google as ...
Cisco Hit by Vishing Attack: CRM Breach Exposes Millions of User Profiles
Cisco has confirmed a new data breach after a vishing (voice phishing) attack tricked a company representative into exposing access to a third-party CRM system. ...
Ox Security Unveils Agent Ox: AI Tool That Writes Tailored Fixes for Software Vulnerabilities
The world of application security is shifting dramatically as AI begins to move from simply flagging vulnerabilities to actively fixing them. Ox Security has launched ...
Meta Deletes 6.8 Million Scam Accounts as AI-Powered Fraud Rings Exploit WhatsApp
Meta has removed 6.8 million accounts tied to criminal scam centers in the first half of 2025, marking one of the most aggressive crackdowns on ...
APT28 / Fancy Bear: Russian State Sponsored APT
APT28, aka Fancy Bear, a Russian GRU-linked group, conducts sophisticated espionage and information theft campaigns globally, targeting governments and critical infrastructure.
Meta Found Liable: Jury Rules Against Tech Giant in Flo Health Privacy Case
In a landmark decision, a California jury has ruled Meta guilty of violating user privacy laws in a class-action lawsuit tied to the popular Flo ...
TSMC Insider Threat: Six Arrested in Taiwan Over 2nm Chip Trade Secrets
In a stunning development, Taiwanese authorities have arrested six individuals suspected of stealing trade secrets from Taiwan Semiconductor Manufacturing Co. (TSMC), the world’s most advanced ...
Approov Secures £5M to Fortify Mobile App and API Security Against AI-Driven Threats
In a major step for mobile and API cybersecurity, Approov, the Edinburgh-based security firm specializing in real-time mobile attestation and API protection, has raised £5 ...
Pwn2Own Ireland 2025: $1M WhatsApp Exploit Bounty Raises the Stakes
This October, Pwn2Own Ireland 2025 will take over Cork with one of the most ambitious cybersecurity competitions yet. Co-sponsored by Meta and organized by Trend ...
FraudOnTok Malware Campaign Targets TikTok Shop Users Through Fake Apps and Phishing Tactics
CTM360 exposes the FraudOnTok campaign targeting TikTok Shop users through fake apps and phishing, using SparkKitty spyware to steal crypto wallet data and drain funds. ...
Palo Alto Networks to Acquire CyberArk in $25 Billion Deal to Strengthen Identity Security
Palo Alto Networks will acquire CyberArk for $25 billion to combine AI-powered security with identity and privilege controls, targeting evolving enterprise threats.
Chanel Confirms US Customer Data Breach Linked to Salesforce Social Engineering Attacks
Chanel confirms a U.S.-based data breach from Salesforce social engineering attacks, exposing contact details amid a broader extortion campaign targeting global enterprise brands.
CurXecute Prompt-Injection Flaw in Cursor IDE Enables Remote Code Execution
Cursor IDE’s CurXecute flaw lets malicious prompts escalate to remote code execution; Pi-hole donor emails leaked via GiveWP plugin misconfiguration. Patches released.
Ransomware Gangs Exploit Microsoft SharePoint Flaws in Widespread Attack Campaign
Ransomware groups are exploiting Microsoft SharePoint flaws in a global attack campaign, affecting over 148 organizations and linking to Chinese state-backed threat actors.
348,000 Patients Impacted in Mt. Baker Imaging Data Breach
A cyberattack on Mt. Baker Imaging exposed sensitive data for 348,000 Washington patients, including medical and financial records, triggering a class action lawsuit.
Everest Ransomware Group Claims Mailchimp but Experts Say Leak Is Minor and Unproven
Everest claims Mailchimp data breach, citing a small internal dataset; security insiders and Intuit report no evidence of systemic compromise.
Akira Ransomware Surges on SonicWall Devices Using Zero-Day and Credential Abuse
A sharp uptick in Akira ransomware activity is exploiting SonicWall remote access infrastructure, potentially via an unpatched zero-day. Akira Ransomware Campaign Intensifies Against SonicWall SSL ...
Attackers Abuse Link-Wrapping Services to Steal Microsoft 365 Credentials
Attackers hijack Proofpoint and Intermedia link-wrapping to hide Microsoft 365 phishing pages, using compromised protected accounts to harvest login credentials.
Nvidia Triton Inference Server Vulnerabilities Expose AI Infrastructure to Attack
A major warning has hit the AI community: Nvidia’s Triton Inference Server — one of the most widely used open-source platforms for deploying and scaling ...