Cyber Security
Signal RingRTC Flaw CVE-2026-113380 Can Keep Mic and Camera On
Exposed Servers Reveal INC and Gentlemen Ransomware AI Operations
WhiteArmour Claims Breach of Disney Staff Directory
Chrome 156 Patches 353 Security Flaws, Six Rated Critical
PHP Warns of Two Critical RCE Flaws as Embargoed Details Leak
DHS Orders Federal Civilian Agencies to Remove DeepSeek Products
Feds Suspect Ransom Negotiator Helped Run ShinyHunters Leak Site
23andMe Successor Settles With California for $6M Over Breach
ICO Reprimands Welsh Bodies After ‘Password1’ Account Breach
Mozilla, Google, Apple Block Eight Weak eMudhra CA Keys
Hacker Claims NBCUniversal Production and Tax-Credit Data Theft
Hijacked Account Plants Stealer in Five OVHcloud CLI Releases
CISA, FBI Say SafePay Ransomware Has Hit 600+ Organizations
Public Exploit Released for Critical FortiSIEM Flaw CVE-2026-106173
State Bank of India Confirms Data Leak of 3,897 Customer Records
Conduent Agrees to $80M Settlement Over Breach of 62M People
Public Exploit Chains 37-Year-Old BSD Bug for OpenBSD Root
OpenCode Silently Patched Critical RCE Flaw With No CVE
Qilin, INC Ransomware Exploit PAN-OS Flaw, Then Pivot to VMware
TeamUpdraft Breach Lets Attackers Backdoor WordPress Sites
Siemens Software Center Flaw Exploited in ROMULUS ClickFix Attacks
Laravel TokenGuard Flaw Lets Attackers Log In as Any User
Roundcube 1.6.20 and 1.7.5 Fix 20 Flaws, Including IMAP Injection
Citizen Lab Confirms Pegasus on Belgrade Rector’s Phone Before Vote
AIA0001 Hacker Uses AI Agents to Breach 100+ Company Websites
Parkview Health Disables Network After Suspicious Activity
Plex2Shell Exploit Chain Hits Plex Servers a Day After PoC Release
Microsoft Confirms Windows Update Breaks Exchange Sign-In, Mail Flow
OpenCode Console Breach May Have Exposed Saved AI Provider API Keys
ConnectWise Cloud Backup Stays Offline After 173 Tenants Hit
Michigan Health System Hack Exposes Patients’ Lab Results in Healthcare Data Breach
Cybersecurity
Michigan Health System Hack Exposes Patients’ Lab Results in Healthcare Data Breach
Aspire Rural Health Systems suffered a major healthcare data breach, exposing nearly 140,000 patients’ records — including lab results, financial data, and personal identifiers.
Gmail Breach Exposes 2.5 Billion Accounts in Social Engineering Attack
Cybersecurity
Gmail Breach Exposes 2.5 Billion Accounts in Social Engineering Attack
Google confirmed a massive breach exposing 2.5 billion Gmail accounts, with hacker group ShinyHunters exploiting Salesforce access through social engineering and launching large-scale phishing and ...
Ethical and Regulatory Challenges in AI-Driven Cybersecurity
Blog
Ethical and Regulatory Challenges in AI-Driven Cybersecurity
As AI becomes central to cybersecurity, it is also weaponized for deepfakes, adaptive malware, and phishing. Organizations now face ethical dilemmas, regulatory fragmentation, and governance ...
AI-Powered DDoS Attacks Prompt Advanced Defense Mechanisms
Blog
AI-Powered DDoS Attacks Prompt Advanced Defense Mechanisms
AI-powered DDoS attacks are reshaping the cybersecurity landscape, replacing brute-force floods with adaptive, machine-led precision. By mimicking legitimate traffic and shifting tactics in real time, ...
Palo Alto Networks Forecasts 10.5B in 2026 Revenue on AI Cybersecurity Growth
Cybersecurity
Palo Alto Networks Forecasts $10.5B in 2026 Revenue on AI Cybersecurity Growth
Palo Alto Networks projects up to $10.53B in fiscal 2026 revenue, fueled by demand for AI cybersecurity tools and strategic acquisitions like CyberArk. With stronger ...
WinRAR Zero-Day Vulnerability Exploited by Multiple Threat Actors
Application Security
WinRAR Zero-Day Vulnerability Exploited by Multiple Threat Actors
A newly discovered zero-day in WinRAR, CVE-2025-8088, is being exploited by RomCom hackers to plant executables in Windows Startup folders via path traversal. The flaw ...
FortiOS Auth Bypass Vulnerability Allows Attackers to Gain Full Control
Cybersecurity
FortiOS Auth Bypass Vulnerability Allows Attackers to Gain Full Control
Fortinet has disclosed CVE-2024-26009, a high-severity authentication bypass in the FGFM protocol. The flaw lets attackers impersonate managed FortiGate devices via FortiManager, enabling full administrative ...
Decline in Cybersecurity Prevention Effectiveness Raises Concerns for CISOs
Blog
Decline in Cybersecurity Prevention Effectiveness Raises Concerns for CISOs
New research from Horizon3.ai, WEF, Trend Micro, and others shows a widening gap between cybersecurity strategies and real-world results. CISOs face declining prevention effectiveness, rising ...
Norway Attributes Dam Cyberattack to Russian Hackers
Cybersecurity
Norway Attributes Dam Cyberattack to Russian Hackers
Norway confirmed that Russian state-sponsored hackers breached the Bremanger dam’s control systems in April 2025, releasing 1.9 million gallons of water. While no damage occurred, ...
Chrome Extension FreeVPN One Secretly Captures Screens
Cybersecurity
Chrome Extension FreeVPN One Secretly Captures Screens
Security researchers found that FreeVPN.One, a Chrome extension with over 100,000 installs and a verified badge, secretly captured user screenshots, URLs, and device data. Updates ...
Critical PostgreSQL Flaws Allow Code Injection During Database Restoration
CVE Vulnerability Alerts
Critical PostgreSQL Flaws Allow Code Injection During Database Restoration
The PostgreSQL team has disclosed three critical vulnerabilities—CVE-2025-8714, CVE-2025-8715, and CVE-2025-1094—impacting backup and restore utilities. These flaws enable malicious code injection and SQL exploitation, posing ...
Internet Archive Abused to Host Stealthy Malware JScript Loaders
Cybersecurity
Internet Archive Abused to Host Stealthy Malware JScript Loaders
Attackers are abusing the Internet Archive to host obfuscated malware loaders, launching multi-stage infection chains that deliver the Remcos RAT. By exploiting trusted infrastructure, threat ...
Business Council of New York State Data Breach: Personal Health Data of 47,000 People Exposed
Cybersecurity
Business Council of New York State Data Breach: Personal Health Data of 47,000 People Exposed
BCNYS reports a two-day February intrusion discovered in August exposed personal, financial, and health data for 47,329 people, prompting rolling notifications and credit monitoring for ...
Cybersecurity
Clickjacking Vulnerability Exposes Autofill Data Across Major Extensions
Attackers use ADFS redirect phishing through legitimate office.com links, bypassing URL filters and MFA, to steal Microsoft 365 logins via malvertising and conditional access tricks.
Financial App Data Leak in Turkey Puts Millions at Risk
Cybersecurity
Financial App Data Leak in Turkey Puts Millions at Risk
An unprotected MongoDB tied to FinansCepte and FinansWebde exposed over four million records, putting Turkish users at risk of phishing, credential stuffing, and manipulated financial ...
GenAI Powers Harder-to-Detect Phishing Threats
News
GenAI Powers Harder-to-Detect Phishing Threats
New research from Unit 42 shows adversaries are combining AI website builders, writing assistants, deepfakes, and chatbots to automate large-scale campaigns that closely mimic trusted ...
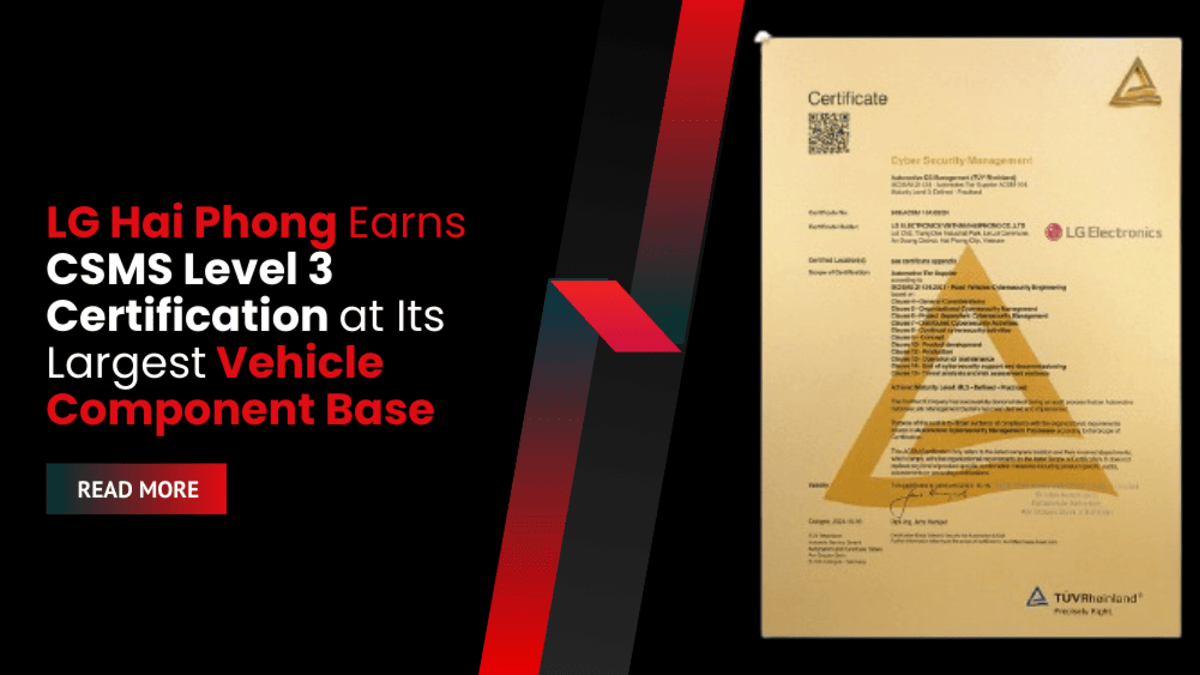
LG Hai Phong Earns CSMS Level 3 Certification at Its Largest Vehicle Component Base
Cybersecurity
LG Hai Phong Earns CSMS Level 3 Certification at Its Largest Vehicle Component Base
LG’s Hai Phong plant earned CSMS Level 3 Certification from TÜV Rheinland, the first facility to hold both Level 2 and Level 3 simultaneously, validating ...
XenoRAT Malware Campaign Targets Embassies in South Korea
Cybersecurity
XenoRAT Malware Campaign Targets Embassies in South Korea
A multi-stage espionage campaign using XenoRAT malware has targeted foreign embassies in South Korea, with evidence linking the activity to both North Korean and Chinese ...
SentinelOne Expands Partnership With Mimecast to Advance People-Focused Cybersecurity
Cybersecurity
SentinelOne Expands Partnership With Mimecast to Advance People-Focused Cybersecurity
SentinelOne and Mimecast deepen integration, pairing Singularity endpoint telemetry with Human Risk Management to prioritize people-focused cybersecurity and reduce human-caused breaches.
Inotiv Ransomware Attack Disrupts Operations After Qilin Claims 176GB Data Theft
News
Inotiv Ransomware Attack Disrupts Operations After Qilin Claims 176GB Data Theft
Inotiv confirms a ransomware attack encrypted systems and data, disrupting operations. SEC filing cites Qilin claims of 176GB theft as investigators restore and assess impact.

Application Security
LiteLLM 1.107.0 Backdoored in PyPI Supply Chain Attack

Cybersecurity
WhiteArmour Claims Breach of Disney Staff Directory

Cybersecurity
Exposed Servers Reveal INC and Gentlemen Ransomware AI Operations
Cybersecurity
CISA, FBI Say SafePay Ransomware Has Hit 600+ Organizations

TOP CYBERSECURITY HEADLINES

This Week’s Security Spotlight

Application Security
PHP Ships Emergency Patches for PHP2Shell as Exploitation Begins

Cybersecurity
CISA, FBI Say SafePay Ransomware Has Hit 600+ Organizations
Cybersecurity
Conduent Agrees to $80M Settlement Over Breach of 62M People
Application Security
Siemens Software Center Flaw Exploited in ROMULUS ClickFix Attacks

Trending

Daily Briefing Newsletter

Subscribe to the Daily Security Review Email Briefing to stay informed on the latest threats, trends, and technology, along with insightful columns from industry experts.

Featured Videos​

  • All
  • Application Security
  • Blog
  • CVE Vulnerability Alerts
  • Cybersecurity
  • Cybersecurity Newsletter
  • Data Security
  • Endpoint Security
  • Identity and Access Management
  • Information Security
  • Network Security
  • News
  • Phishing
  • Podcasts
  • Product Reviews
  • Ransomware
  • Ransomware Victims
  • Resources
  • Security Spotlight
  • Sponsored
  • Threat Actors
  • Threat Actors
  • Threat Detection Tools
Salesloft Data Breach Exposes 700 Companies Through OAuth Token Attack
A major security breach at Salesloft has compromised sensitive information from more than 700 companies, marking one of the largest enterprise incidents linked to OAuth ...
U.S. Charges Ukrainian National for Administering Ransomware
The U.S. charged Ukrainian national Volodymyr Tymoshchuk for administering LockerGoga, MegaCortex, and Nefilim ransomware, linked to hundreds of corporate breaches and millions in damages worldwide.
Doctors Outraged After NSW Health Department Leaks Personal and Professional Data
NSW Health exposed passports, medical credentials, and IDs of nearly 600 doctors, sparking outrage and raising serious risks of identity theft, fraud, and professional impersonation.
Salt Typhoon Breach Exposes U.S. Telecom Wiretap Systems
Chinese-linked APT group Salt Typhoon infiltrated major U.S. telecom providers in 2024, compromising surveillance systems and metadata from millions of users. The breach exposed lawful ...
China Is Blurring the Lines Between Civilian AI and Military Power
China is merging civilian AI with military applications. Everyday tools like drones and voice apps are being leveraged by the PLA, according to a CSET ...
Rose Acre Farms Targeted in Alleged Lynx Ransomware Attack
Rose Acre Farms, America’s second-largest egg producer, was allegedly hit by Lynx ransomware, with attackers claiming encrypted data in a breach that threatens food supply ...
Lovesac Confirms Data Breach Following Ransomware Attack
Lovesac confirmed a ransomware-linked data breach impacting personal information. Attackers accessed systems in February 2025, with stolen data linked to the RansomHub ransomware group’s extortion ...
GhostAction Supply Chain Attack on GitHub Exposes 3,325 Secrets
The GhostAction supply chain attack on GitHub compromised 3,325 secrets, including npm, PyPI, AWS, and GitHub tokens, after attackers injected malicious workflows into 817 repositories.
Qantas Airways Reduces CEO’s Bonus Following July Data Breach
Qantas Airways reduced CEO Vanessa Hudson’s pay by $250,000 following a July cyber attack that exposed 4.5 million customer records, reflecting leadership accountability and strengthened ...
The “s1ngularity” Attack: How Hackers Hijacked Nx and Leaked Thousands of Repositories
In late August 2025, the open-source software ecosystem was rocked by a sophisticated two-phase supply chain attack, now known as “s1ngularity.” The incident began when ...
Canadian Investment Giant Wealthsimple Hit by Vendor Compromise
Wealthsimple, one of Canada’s largest online investment platforms, has confirmed a data breach that exposed the sensitive information of fewer than 1% of its three ...
FireCompass Raises $20M to Scale AI-Powered Offensive Security
In a year when cybercrime is projected to cost the world over $10.5 trillion, FireCompass has emerged as one of the most closely watched AI-driven ...
CVE-2025-42957: Active Exploits Target SAP S/4HANA Systems
A newly uncovered critical vulnerability, tracked as CVE-2025-42957, is sending shockwaves through the enterprise technology world. Affecting all SAP S/4HANA deployments, both on-premise and in ...
Fake Job Interviews, Real Hacks: How North Korean Spies Steal Billions in Crypto
North Korean cybercriminals have escalated their social engineering operations, deploying a wave of sophisticated campaigns designed to infiltrate cryptocurrency and decentralized finance (DeFi) organizations. At ...
North Korean Hackers Pose as Recruiters To Launch Global Cyberattacks
North Korean hackers posed as recruiters to target blockchain and finance professionals, exploiting Slack and cyber intelligence platforms to steal cryptocurrency in a global campaign ...
Social Engineering Breach Opens Door to Google Salesforce Data Leak
A phishing attack on a Google employee led to a Salesforce breach, exposing business contact data. Gmail remained secure, but the incident underscores the power ...
Czech Cybersecurity Agency Warns Against Chinese Technology in Critical Infrastructure
The Czech Republic’s cybersecurity agency warns critical infrastructure operators against Chinese technology, elevates threat level to “High,” and cites confirmed malicious activity, data access risks, ...
This Week In Cybersecurity: September 1–5, 2025
News Stories Jaguar Land Rover Cyberattack Severely Disrupts Production Systems Taken Offline Jaguar Land Rover halted operations after a cyberattack disabled its production systems, forcing ...
Cybersecurity Leadership: An Expert Talks Executive Risk
Leah Santos, CISO and Cyber Resilience Advisor Talks Executive Risk
Wealthsimple Data Breach Leaked Client Information Online
Wealthsimple confirmed a September 2025 data breach affecting under one percent of clients. Personal details were exposed, but passwords and funds remained fully secure throughout ...