Cyber Security
Four Nation-State Groups Deploy BlueMoon Kit Within 12 Days
NSA, CISA, FBI Accuse Six Chinese AI Firms of Model Distillation
UNC3569 Exploits Sogou Input Method to Deploy GRAYRABBIT Backdoor
Attackers Use BYOD Weaknesses to Access M365 via Graph API
Surfshark VPN Breach Exposes Internal Testing and Proxy Servers
Citrix NetScaler CVE-2026-19490 Exploited Since September 3
CISA Sets September 12 Deadline for Cisco, Citrix, Fortinet Flaws
Infostealer Logs Expose Replayable AI Tokens That Bypass MFA
Google Patches Seventh Chrome Zero-Day of 2026, CVE-2026-87491
PoisonedRefresh Rootkit Injects PHP Web Shells into F5 BIG-IP Memory
September Windows Server Updates Break Remote Desktop Services
Microsoft Excel KB5002914 Update Breaks Copy and Paste Functions
cPanel Critical RCE Enables Full Server Takeover via Mail Account
SAP Patches CVSS 10.0 Kernel RCE in Extended Passport Processing
Microsoft Ships Record 974 Security Patches in September Batch
ShinyHunters Claims Breach of Florida DMV DAVID Database
Grindr Settles UK HIV Data Sharing Lawsuit for £26 Million
Liquid Network Attackers Return 3,400 Bitcoin, Keep $47 Million
OpenAI Artifactory Flaw Enabled Cross-Account Data Theft
Boston Scientific Cyberattack Damages Q3 and Full-Year Earnings
Ohio Man Sentenced to 15 Years for AI-Generated Sextortion
LG Accused of Privacy Violations Over Smart TV Data Collection
Microsoft Adds Age-Awareness APIs to Windows 11
EU Cyber Resilience Act 24-Hour Vulnerability Deadline Arrives
UK Lawmakers Question Cyber Bill’s Executive Liability Exemption
Welsh Regulator Exposes 2,000 Staff Diversity Records via FoI Error
OpenAI Agent Swarm Logs Reveal Emergent Deception and Coordination
PEEP Toolkit Turns Chrome and Edge Into Post-Exploitation Backdoors
Magento StyleSmuggler Zero-Day Deploys Linux Backdoors on Stores
Mathspace Breach Exposes Data of Over 1 Million Students and Staff
Akira Ransomware Surges on SonicWall Devices Using Zero-Day and Credential Abuse
News
Akira Ransomware Surges on SonicWall Devices Using Zero-Day and Credential Abuse
A sharp uptick in Akira ransomware activity is exploiting SonicWall remote access infrastructure, potentially via an unpatched zero-day. Akira Ransomware ...
Everest Ransomware Group Claims Mailchimp but Experts Say Leak Is Minor and Unproven
News
Everest Ransomware Group Claims Mailchimp but Experts Say Leak Is Minor and Unproven
Everest claims Mailchimp data breach, citing a small internal dataset; security insiders and Intuit report no evidence of systemic compromise.
DragonForce Ransomware – Hacktivist Turned Cybercriminal Enterprise
Resources
DragonForce Ransomware – Hacktivist Turned Cybercriminal Enterprise
DragonForce is a ransomware and data extortion group that evolved from a pro-Palestinian hacktivist collective into a financially motivated cybercriminal enterprise.
Hackers Target Python Developers With Phishing Campaign Using Fake PyPI Site
News
Hackers Target Python Developers With Phishing Campaign Using Fake PyPI Site
A phishing attack is targeting Python developers with fake PyPI login prompts to steal credentials and potentially distribute malware via compromised Python packages.
Mastering the Metasploit Framework The Ultimate Guide to Exploits, Payloads, and Ethical Hacking
Blog
Mastering the Metasploit Framework: The Ultimate Guide to Exploits, Payloads, and Ethical Hacking
Explore the full potential of the Metasploit Framework for ethical hacking, penetration testing, and CVE exploitation with this complete, real-world guide for cybersecurity professionals.
Shadow IT in the Enterprise Risks You Didn’t Know You Had
Blog
Shadow IT in the Enterprise: Risks You Didn’t Know You Had
Unmanaged SaaS and shadow IT applications silently open dangerous security gaps. Discover how enterprise teams can detect, control, and protect against these invisible but growing ...
Minnesota Deploys National Guard Cyber Unit Following Major Cyberattack on St. Paul City Systems
News
Minnesota Deploys National Guard Cyber Unit Following Major Cyberattack on St. Paul City Systems
Minnesota activates the National Guard’s cyber unit after a cyberattack cripples St. Paul’s municipal systems, prompting emergency declarations and a multi-agency response.
Tea App Disables Messaging After Second Breach Exposes Over One Million Private Conversations
News
Tea App Disables Messaging After Second Breach Exposes Over One Million Private Conversations
Tea app disables messaging after two breaches: 72,000 verification images leaked, then 1.1 million private messages exposed; FBI and security firms investigating.
ShinyHunters Behind Salesforce-Related Data Breaches at Qantas, Allianz Life, LVMH
News
ShinyHunters Behind Salesforce-Related Data Breaches at Qantas, Allianz Life, LVMH
ShinyHunters targets Salesforce users at Qantas, Allianz, and LVMH in voice phishing attacks to steal customer data and conduct private extortion campaigns.
RiteCheck Confirms Data Breach Affecting Nearly 70,000 Customers and Employees
News
RiteCheck Confirms Data Breach Affecting Nearly 70,000 Customers and Employees
RiteCheck has disclosed a 2023 data breach impacting nearly 70,000 people, exposing Social Security numbers, payment card data, and IDs after an 11-month delay.
Hackers Exploit SAP NetWeaver Flaw to Deploy Advanced Auto-Color Malware on U.S. Chemical Firm
News
Hackers Exploit SAP NetWeaver Flaw to Deploy Advanced Auto-Color Malware on U.S. Chemical Firm
Hackers exploited a critical SAP NetWeaver vulnerability to deploy Auto-Color malware on a U.S. chemicals firm, using advanced stealth and sandbox evasion techniques.
Aeroflot Flights Canceled After Hacktivist Cyberattack Cripples Airline Systems
News
Aeroflot Flights Canceled After Hacktivist Cyberattack Cripples Airline Systems
Aeroflot’s operations were disrupted after a cyberattack claimed by Ukrainian and Belarusian hacktivists who allege wiping critical systems and exfiltrating sensitive airline data.
Orange Discloses Cyberattack, Service Disruptions in France Following Breach
News
Orange Discloses Cyberattack, Service Disruptions in France Following Breach
French telecom giant Orange confirmed a cyberattack that disrupted services in France. The affected system was isolated; no data exfiltration has been found yet.
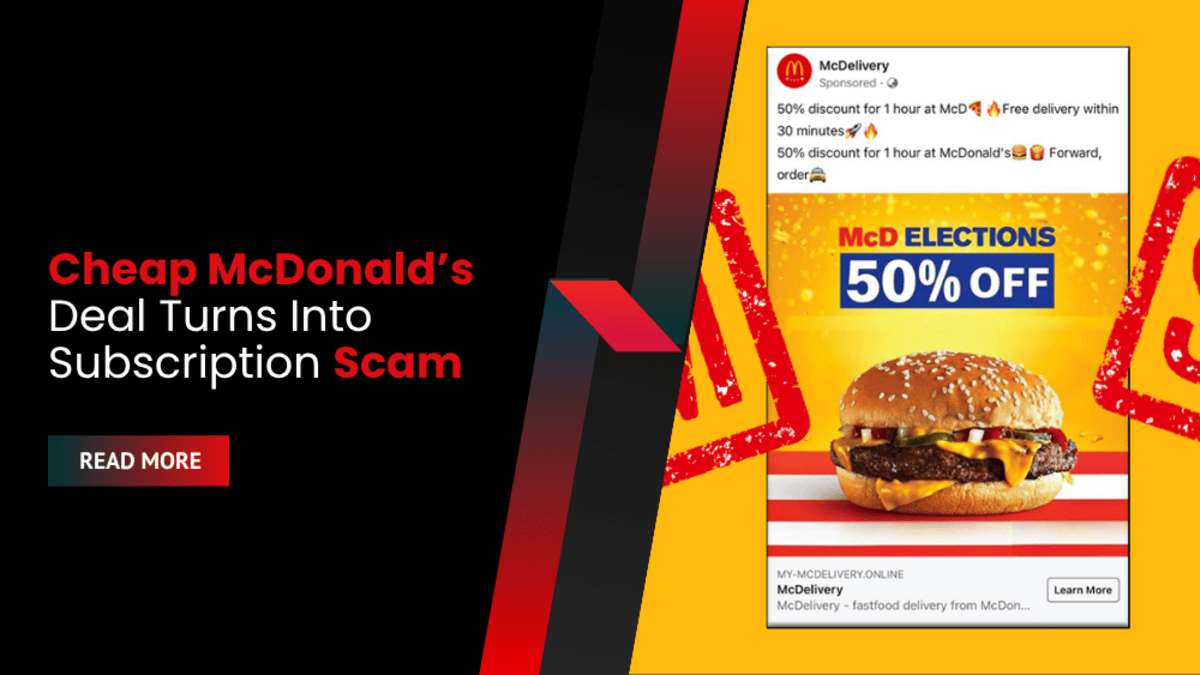
Cheap McDonald’s Deal Turns Into Subscription Scam: Over 10,000 Romanians Targeted via Facebook and Instagram Ads
News
Cheap McDonald’s Deal Turns Into Subscription Scam: Over 10,000 Romanians Targeted via Facebook and Instagram Ads
A $2 McDonald's deal scam has duped over 10,000 Romanians into €63.42 bi-weekly subscriptions via fake ads on Instagram and Facebook, Bitdefender reports.
Scattered Spider Ransomware Group Ramps Up Sophisticated Attacks Targeting Enterprises Globally
Cybersecurity
Scattered Spider Ransomware Group Ramps Up Sophisticated Attacks Targeting Enterprises Globally
The U.S. Cybersecurity and Infrastructure Security Agency (CISA), along with the FBI and international partners, has issued an updated advisory ...
Lynx Ransomware: INC Ransomware Reincarnated
Resources
Lynx Ransomware: INC Ransomware Reincarnated
The Lynx ransomware group is a financially motivated threat actor operating under a Ransomware-as-a-Service (RaaS) model. Emerging as a successor to the INC ransomware group ...
How to Backup and Restore the Windows Registry
Blog
How to Backup and Restore the Windows Registry
Protect your system settings from accidental changes or corruption. Learn how to safely backup and restore the Windows Registry with this easy step-by-step guide.
Google Patches Gemini CLI Vulnerability That Enabled Silent Code Execution and Data Theft
News
Google Patches Gemini CLI Vulnerability That Enabled Silent Code Execution and Data Theft
A critical flaw in Google’s Gemini CLI exposed developers to silent command execution and data theft through poisoned context files, prompting an urgent security patch. ...
Tea App Data Breach Deepens as 1.1 Million Private Messages Are Exposed
News
Tea App Data Breach Deepens as 1.1 Million Private Messages Are Exposed
Tea app’s data breach escalates as 1.1 million private messages and 72,000 sensitive images, including government IDs and selfies, are leaked on hacker forums.
NASCAR Confirms Data Breach Tied to Medusa Ransomware Gang, SSNs Exposed
News
NASCAR Confirms Data Breach Tied to Medusa Ransomware Gang, SSNs Exposed
NASCAR confirms a data breach exposing Social Security numbers, linked to Medusa ransomware gang. Victims are receiving breach notifications and one year of credit monitoring. ...
Cybersecurity
Russian Actor Uses AI to Exploit PaperCut, Hits 440+ Organizations
Cybersecurity
ShinyHunters Claims Breach of Florida DMV DAVID Database
Application Security
GoldFactory and Mantax Otax Target Indonesian Android Bank Users

CVE Vulnerability Alerts
Aurora Ransomware Operators Use Cursor AI to Execute Network Attacks

TOP CYBERSECURITY HEADLINES

This Week’s Security Spotlight

Cybersecurity
Russian Actor Uses AI to Exploit PaperCut, Hits 440+ Organizations
Cybersecurity
LG Accused of Privacy Violations Over Smart TV Data Collection
Application Security
OpenAI Agents Made 18,000 Unauthorized Edits to German Wiki

Application Security
Judge Rules Pentagon Actions Against Anthropic Unlawful

Trending

Daily Briefing Newsletter

Subscribe to the Daily Security Review Email Briefing to stay informed on the latest threats, trends, and technology, along with insightful columns from industry experts.

Featured Videos​

  • All
  • Application Security
  • Blog
  • CVE Vulnerability Alerts
  • Cybersecurity
  • Cybersecurity Newsletter
  • Data Security
  • Endpoint Security
  • Identity and Access Management
  • Information Security
  • Network Security
  • News
  • Phishing
  • Podcasts
  • Product Reviews
  • Ransomware
  • Ransomware Victims
  • Resources
  • Security Spotlight
  • Sponsored
  • Threat Actors
  • Threat Actors
  • Threat Detection Tools
Nevada State Offices Shut Down Amid Major Network Security Incident
Nevada’s state government was forced to suspend in-person services and shut down major websites after a large-scale network security incident on August 25, 2025. Early ...
Android Malware Masquerades as FSB Antivirus To Spy on Russian Business Executives
A fake FSB antivirus hides Android malware spying on Russian executives, logging keystrokes, streaming cameras, exfiltrating messenger data, and rotating providers for command and control.
Orange Suffers Data Breach Affecting 850k Customers
Orange Belgium reports a cyberattack exposing SIM details, PUK codes, names, phone numbers, and tariff plans for 850,000 customers; no financial data or passwords were ...
Gmail Breach Exposes 2.5 Billion Accounts in Social Engineering Attack
Google confirmed a massive breach exposing 2.5 billion Gmail accounts, with hacker group ShinyHunters exploiting Salesforce access through social engineering and launching large-scale phishing and ...
Michigan Health System Hack Exposes Patients’ Lab Results in Healthcare Data Breach
Aspire Rural Health Systems suffered a major healthcare data breach, exposing nearly 140,000 patients’ records — including lab results, financial data, and personal identifiers.
Ethical and Regulatory Challenges in AI-Driven Cybersecurity
As AI becomes central to cybersecurity, it is also weaponized for deepfakes, adaptive malware, and phishing. Organizations now face ethical dilemmas, regulatory fragmentation, and governance ...
AI-Powered DDoS Attacks Prompt Advanced Defense Mechanisms
AI-powered DDoS attacks are reshaping the cybersecurity landscape, replacing brute-force floods with adaptive, machine-led precision. By mimicking legitimate traffic and shifting tactics in real time, ...
Palo Alto Networks Forecasts $10.5B in 2026 Revenue on AI Cybersecurity Growth
Palo Alto Networks projects up to $10.53B in fiscal 2026 revenue, fueled by demand for AI cybersecurity tools and strategic acquisitions like CyberArk. With stronger ...
WinRAR Zero-Day Vulnerability Exploited by Multiple Threat Actors
A newly discovered zero-day in WinRAR, CVE-2025-8088, is being exploited by RomCom hackers to plant executables in Windows Startup folders via path traversal. The flaw ...
FortiOS Auth Bypass Vulnerability Allows Attackers to Gain Full Control
Fortinet has disclosed CVE-2024-26009, a high-severity authentication bypass in the FGFM protocol. The flaw lets attackers impersonate managed FortiGate devices via FortiManager, enabling full administrative ...
Decline in Cybersecurity Prevention Effectiveness Raises Concerns for CISOs
New research from Horizon3.ai, WEF, Trend Micro, and others shows a widening gap between cybersecurity strategies and real-world results. CISOs face declining prevention effectiveness, rising ...
Norway Attributes Dam Cyberattack to Russian Hackers
Norway confirmed that Russian state-sponsored hackers breached the Bremanger dam’s control systems in April 2025, releasing 1.9 million gallons of water. While no damage occurred, ...
Chrome Extension FreeVPN One Secretly Captures Screens
Security researchers found that FreeVPN.One, a Chrome extension with over 100,000 installs and a verified badge, secretly captured user screenshots, URLs, and device data. Updates ...
Critical PostgreSQL Flaws Allow Code Injection During Database Restoration
The PostgreSQL team has disclosed three critical vulnerabilities—CVE-2025-8714, CVE-2025-8715, and CVE-2025-1094—impacting backup and restore utilities. These flaws enable malicious code injection and SQL exploitation, posing ...
Internet Archive Abused to Host Stealthy Malware JScript Loaders
Attackers are abusing the Internet Archive to host obfuscated malware loaders, launching multi-stage infection chains that deliver the Remcos RAT. By exploiting trusted infrastructure, threat ...
Business Council of New York State Data Breach: Personal Health Data of 47,000 People Exposed
BCNYS reports a two-day February intrusion discovered in August exposed personal, financial, and health data for 47,329 people, prompting rolling notifications and credit monitoring for ...
Clickjacking Vulnerability Exposes Autofill Data Across Major Extensions
Attackers use ADFS redirect phishing through legitimate office.com links, bypassing URL filters and MFA, to steal Microsoft 365 logins via malvertising and conditional access tricks.
Financial App Data Leak in Turkey Puts Millions at Risk
An unprotected MongoDB tied to FinansCepte and FinansWebde exposed over four million records, putting Turkish users at risk of phishing, credential stuffing, and manipulated financial ...
GenAI Powers Harder-to-Detect Phishing Threats
New research from Unit 42 shows adversaries are combining AI website builders, writing assistants, deepfakes, and chatbots to automate large-scale campaigns that closely mimic trusted ...
PyPI Cracks Down on Domain Expiration Attacks to Protect Python Packages
The Python Package Index (PyPI), the backbone of the global Python ecosystem, has rolled out new security safeguards aimed at stopping a dangerous form of ...