Cyber Security
23andMe Successor Settles With California for $6M Over Breach
ICO Reprimands Welsh Bodies After ‘Password1’ Account Breach
Mozilla, Google, Apple Block Eight Weak eMudhra CA Keys
Hacker Claims NBCUniversal Production and Tax-Credit Data Theft
Hijacked Account Plants Stealer in Five OVHcloud CLI Releases
CISA, FBI Say SafePay Ransomware Has Hit 600+ Organizations
Public Exploit Released for Critical FortiSIEM Flaw CVE-2026-106173
State Bank of India Confirms Data Leak of 3,897 Customer Records
Conduent Agrees to $80M Settlement Over Breach of 62M People
Public Exploit Chains 37-Year-Old BSD Bug for OpenBSD Root
OpenCode Silently Patched Critical RCE Flaw With No CVE
Qilin, INC Ransomware Exploit PAN-OS Flaw, Then Pivot to VMware
TeamUpdraft Breach Lets Attackers Backdoor WordPress Sites
Siemens Software Center Flaw Exploited in ROMULUS ClickFix Attacks
Laravel TokenGuard Flaw Lets Attackers Log In as Any User
Roundcube 1.6.20 and 1.7.5 Fix 20 Flaws, Including IMAP Injection
Citizen Lab Confirms Pegasus on Belgrade Rector’s Phone Before Vote
AIA0001 Hacker Uses AI Agents to Breach 100+ Company Websites
Parkview Health Disables Network After Suspicious Activity
Plex2Shell Exploit Chain Hits Plex Servers a Day After PoC Release
Microsoft Confirms Windows Update Breaks Exchange Sign-In, Mail Flow
OpenCode Console Breach May Have Exposed Saved AI Provider API Keys
ConnectWise Cloud Backup Stays Offline After 173 Tenants Hit
Unpatched Broadcom WPS Flaw Lets Nearby Attackers Root Routers
Drupal Patches Two Critical RCE Flaws, Warns Exploits Could Follow
Trojanized Rank Math SEO PRO 3.0.123 Backdoors WordPress Sites
Apache Fixes 12 Kylin Flaws, Including Critical SQL Injection
CISA Flags dcm4chee Archive Flaws and Unpatched EseeCloud Cameras
Infinity Core Research Publishes Exploits for Six Linux Kernel Flaws
California Student Records Exposed in ETS SFTP Breach
Baltimore City Public Schools Data Breach Impacts 25,000 Individuals After Ransomware Attack
News
Baltimore City Public Schools Data Breach Impacts 25,000 Individuals After Ransomware Attack
Baltimore City Public Schools confirms 25,000 people were impacted by a February ransomware attack that exposed sensitive employee and student information, including identification documents.
Active! Mail Zero-Day RCE Vulnerability Exploited in Ongoing Attacks on Japanese Organizations
News
Active! Mail Zero-Day RCE Vulnerability Exploited in Ongoing Attacks on Japanese Organizations
A zero-day flaw in Active! Mail is under active exploitation in Japan, affecting major providers and exposing data across enterprise, education, and government sectors.
Ad Fraud Operation 'Scallywag' Used WordPress Plugins to Generate 1.4 Billion Daily Ad Requests
Cybersecurity
Ad Fraud Operation ‘Scallywag’ Used WordPress Plugins to Generate 1.4 Billion Daily Ad Requests
The Scallywag ad fraud network used WordPress plugins to generate 1.4 billion daily ad requests, monetizing piracy and redirect sites before being dismantled.
FBI Warns of IC3 Impersonation Scam Targeting Victims of Online Fraud
Cybersecurity
FBI Warns of IC3 Impersonation Scam Targeting Victims of Online Fraud
The FBI warns of a scam where criminals impersonate IC3 officials, targeting prior fraud victims with false promises of fund recovery to steal financial information. ...
Abilene, Texas Shuts Down City Systems Following Cyberattack
News
Abilene, Texas Shuts Down City Systems Following Cyberattack
Abilene, Texas has taken key systems offline after a cyberattack. City services are disrupted but emergency response remains intact. Investigation and recovery efforts continue.
Google Confirms Sophisticated Phishing Attack Targeting Gmail Users Through DKIM and OAuth Abuse
News
Google Confirms Sophisticated Phishing Attack Targeting Gmail Users Through DKIM and OAuth Abuse
Google confirms a phishing campaign targeting Gmail users that abused DKIM and Google Sites to send spoofed legal requests and steal user credentials undetected.
Imaflex Inc. Data Breach Exposes Personal and Employment Data
News
Imaflex Inc. Data Breach Exposes Personal and Employment Data
Imaflex Inc. Data Breach Exposes Personal and Employment Data: Legal Investigation Underway Imaflex Inc. has disclosed a data breach that exposed sensitive personal and employment-related ...
Evil Corp (UNC2165): The Russian Syndicate Behind Global Cyber Chaos
Resources
Evil Corp (UNC2165): The Russian Syndicate Behind Global Cyber Chaos
Evil Corp, a prolific Russian cybercrime syndicate, deploys sophisticated malware and ransomware, targeting diverse sectors globally, including healthcare and finance, for financial gain and potential ...
Cybersecurity Newsletter
This Week In Cybersecurity: April 1st to 5th, 2025
This week in cybersecurity covers a range of incidents, including the shutdown of openSNP over privacy concerns, a data breach affecting 173,000 patients, and a ...
This Week In Cybersecurity: 03rd March to 07th March
Cybersecurity Newsletter
This Week In Cybersecurity: March 3rd to 7th, 2025
This Week in Cybersecurity: Data Breaches, Ransomware, Threat Actors, Ransomware Protection and more!
Ransomware Victims on Dark Web – 10th March, 2025
News
Ransomware Victims on Dark Web – 10th March, 2025
This report summarizes recent ransomware attacks across various sectors, detailing the victims, threat actors, and available information on the incidents. Due to the nature of ...
Ransomware Victims on Dark Web – 04th March, 2025
Ransomware
Ransomware Victims on Dark Web – 04th March, 2025
This report summarizes recent ransomware attacks across various sectors, detailing the victims, threat actors, and available information on the incidents. Due to the nature of ...
Ransomware Victims on Dark Web – 04th March, 2025
Ransomware Victims
Ransomware Victims on Dark Web – 05th March, 2025
This report summarizes recent ransomware attacks across various sectors, detailing the victims, threat actors, and available information on the incidents. ...
Ransomware Victims on Dark Web – 06th March, 2025
Ransomware Victims
Ransomware Victims on Dark Web – 06th March, 2025
This report summarizes recent ransomware attacks across various sectors, detailing the victims, threat actors, and available information on the incidents. ...
Remote Desktop Protocol (RDP) A Double-Edged Sword for IT Teams
Blog
Remote Desktop Protocol (RDP): A Double-Edged Sword for IT Teams
Secure your Remote Desktop Protocol (RDP) with these essential tips. Learn how to mitigate risks and protect your systems from cyberattacks targeting RDP vulnerabilities.
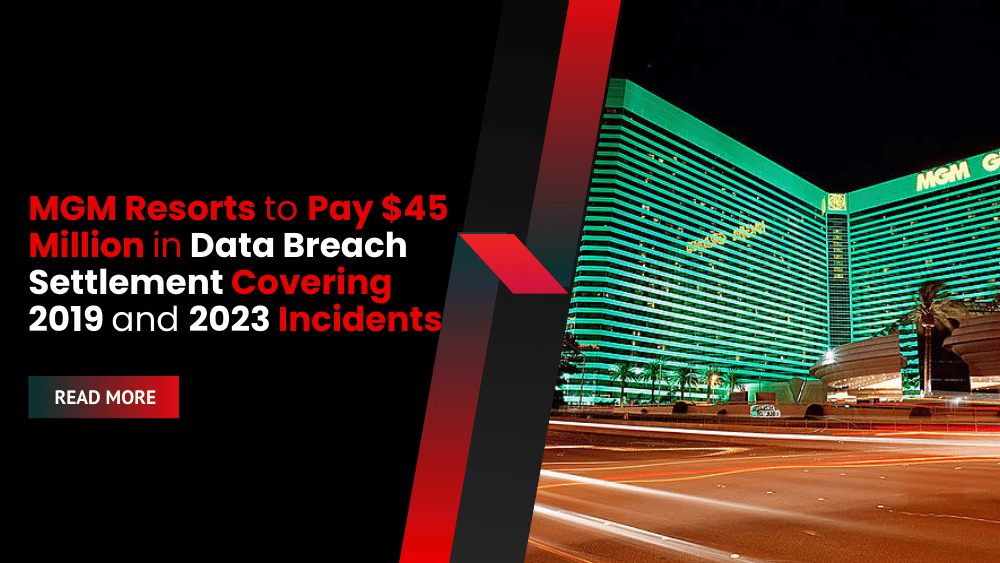
MGM Resorts to Pay $45 Million in Data Breach Settlement Covering 2019 and 2023 Incidents
News
MGM Resorts to Pay $45 Million in Data Breach Settlement Covering 2019 and 2023 Incidents
MGM Resorts will pay $45 million to settle a lawsuit over data breaches in 2019 and 2023, offering up to $75 per affected individual.
Attackers Abuse Google OAuth in Sophisticated DKIM Replay Phishing Scheme
News
Attackers Abuse Google OAuth in Sophisticated DKIM Replay Phishing Scheme
Attackers exploited Google’s OAuth and DKIM signing process to send phishing emails that appeared authentic, bypassing traditional security checks and targeting unsuspecting recipients.
New Android Malware 'SuperCard X' Enables NFC Relay Attacks for Payment Card Theft
News
New Android Malware ‘SuperCard X’ Enables NFC Relay Attacks for Payment Card Theft
A new Android malware called SuperCard X enables NFC relay attacks by stealing card data via fake banking support calls and emulating it on attacker ...
State-Backed Threat Actors Adopt ClickFix Social Engineering in Espionage Campaigns
News
State-Backed Threat Actors Adopt ClickFix Social Engineering in Espionage Campaigns
State-backed hackers from North Korea, Iran, and Russia are now using ClickFix, a social engineering method that tricks users into manually executing malware payloads.
Interlock Ransomware Gang Deploys ClickFix Attacks Using Fake IT Tools to Compromise Networks
News
Interlock Ransomware Gang Deploys ClickFix Attacks Using Fake IT Tools to Compromise Networks
Interlock ransomware operators now use ClickFix attacks with fake IT tools to deploy malware, exfiltrate data, and encrypt systems, targeting corporate environments through social engineering. ...

Application Security
PHP Warns of Two Critical RCE Flaws as Embargoed Details Leak

Cybersecurity
CISA, FBI Say SafePay Ransomware Has Hit 600+ Organizations
CVE Vulnerability Alerts
Qilin, INC Ransomware Exploit PAN-OS Flaw, Then Pivot to VMware

TOP CYBERSECURITY HEADLINES

This Week’s Security Spotlight

Cybersecurity
CISA, FBI Say SafePay Ransomware Has Hit 600+ Organizations
Cybersecurity
Conduent Agrees to $80M Settlement Over Breach of 62M People
Application Security
Siemens Software Center Flaw Exploited in ROMULUS ClickFix Attacks

Application Security
Microsoft Confirms Windows Update Breaks Exchange Sign-In, Mail Flow

Trending

Daily Briefing Newsletter

Subscribe to the Daily Security Review Email Briefing to stay informed on the latest threats, trends, and technology, along with insightful columns from industry experts.

Featured Videos​

Podcasts

Sorry, we couldn't find any posts. Please try a different search.

  • All
  • Application Security
  • Blog
  • CVE Vulnerability Alerts
  • Cybersecurity
  • Cybersecurity Newsletter
  • Data Security
  • Endpoint Security
  • Identity and Access Management
  • Information Security
  • Network Security
  • News
  • Phishing
  • Podcasts
  • Product Reviews
  • Ransomware
  • Ransomware Victims
  • Resources
  • Security Spotlight
  • Sponsored
  • Threat Actors
  • Threat Actors
  • Threat Detection Tools
Bonfy.AI Launches $9.5M Adaptive Content Security Platform to Govern AI and Human Data
In a major development at the intersection of cybersecurity and AI governance, Israeli startup Bonfy.AI has officially launched its adaptive content security platform, backed by ...
Central Kentucky Radiology’s 2024 Data Breach Affects 167,000
In October 2024, Central Kentucky Radiology (CKR), a Lexington-based imaging provider, became the latest victim of a growing trend in healthcare cyberattacks. An unauthorized actor ...
Why External Attack Surface Management Belongs at the Core of Your Cybersecurity Strategy
Discover why External Attack Surface Management (EASM) is vital for modern digital risk protection and how it enhances visibility, threat detection, and cyber resilience strategies. ...
Pro-Russian Hackers Disrupt Dutch Government Websites Amid Heightened NATO Security
Pro-Russian hacker group NoName057(16) claims responsibility for a DDoS attack that disrupted Dutch municipal websites during the NATO Summit’s peak security deployment.
OneClik Campaign Exploits Microsoft ClickOnce and AWS to Breach Energy and Industrial Networks
A stealthy malware campaign abuses Microsoft ClickOnce and AWS services to deploy Golang-based RunnerBeacon backdoors targeting energy and industrial organizations with advanced evasion techniques.
French Authorities Arrest BreachForums v2 Operators Behind Global Data Theft Campaigns
French police arrest BreachForums v2 operators, including ShinyHunters and IntelBroker, tied to major global and national data breaches affecting millions of users and enterprises.
Hacker ‘IntelBroker’ Indicted in $25M Global Data Theft Campaign
British hacker ‘IntelBroker’ charged by U.S. authorities for stealing and selling sensitive data worldwide, causing $25 million in damage to governments and global enterprises.
CISA Confirms Active Exploitation of Critical AMI MegaRAC BMC Vulnerability Enabling Remote Server Hijack
CISA confirms that a critical vulnerability in AMI MegaRAC BMC firmware is being exploited to hijack servers remotely, prompting urgent patching across government and enterprise ...
Columbia University Struggles to Restore Services Following Suspected Cyberattack
Columbia University is working to restore critical systems following a suspected cyberattack that has caused widespread outages, impacting thousands of students and faculty.
U.S. Government Pushes Back on Meta: WhatsApp Labeled a High-Risk App
The U.S. House of Representatives has officially banned the use of WhatsApp on all House-managed devices, citing significant data security risks. This move places WhatsApp ...
How Cyberattacks on Mainline Health and Select Medical Exposed Over 200,000 Patients
The healthcare industry is facing a relentless wave of cyber threats, as demonstrated by two recent breaches impacting Mainline Health Systems and Select Medical Holdings. ...
Scattered Spider: The Threat You Think You Know
Scattered Spider isn’t a single group but a sprawling web of identity-based attackers exploiting help desks, MFA gaps, and cloud admin tools to breach enterprises. ...
New FileFix Attack Exploits Windows File Explorer to Deliver Stealthy Commands
A researcher has revealed a new FileFix attack that abuses Windows File Explorer’s address bar to stealthily execute commands, expanding on previous ClickFix phishing techniques. ...
Trojanized SonicWall NetExtender Client Targets VPN Credentials via Spoofed Sites
SonicWall and Microsoft have discovered a trojanized version of the NetExtender VPN client being distributed via spoofed websites, stealing remote access credentials from unsuspecting users. ...
Two Healthcare Data Breaches Expose Over 220,000 Records at Mainline Health and Select Medical
Mainline Health and Select Medical Holdings have disclosed separate data breaches impacting more than 220,000 individuals, with ransomware and third-party compromise behind the incidents.
New Spear Phishing Campaign Targets Financial Executives Using Legitimate Remote Access Tools
A sophisticated spear phishing campaign is targeting CFOs and finance leaders worldwide, using legitimate tools like NetBird and OpenSSH to quietly breach enterprise networks.
The Siemens-Microsoft Antivirus Dilemma Threatening OT Security
This episode examines a serious conflict between Siemens’ Simatic PCS industrial control systems and Microsoft Defender Antivirus. The absence of an “alert only” mode in ...
Prometei Botnet’s Global Surge: A Threat to Linux and Windows Systems Alike
Prometei is one of the most persistent and sophisticated botnet threats in circulation today. First identified in 2020—and active since at least 2016—this modular malware ...
UK Government Warns of £1.6 Million in Ticket Scams Ahead of Glastonbury Festival
Concertgoers in the UK have lost over £1.6 million to ticket fraud in 2024, prompting urgent warnings from the government as festival season begins.
Patient Trust on the Line: The Fallout from McLaren Health Care’s 2024 Breach
In this episode, we dive into the 2024 McLaren Health Care data breach that compromised the sensitive information of over 743,000 individuals—just one year after ...