Cyber Security
Signal RingRTC Flaw CVE-2026-113380 Can Keep Mic and Camera On
Exposed Servers Reveal INC and Gentlemen Ransomware AI Operations
WhiteArmour Claims Breach of Disney Staff Directory
Chrome 156 Patches 353 Security Flaws, Six Rated Critical
PHP Warns of Two Critical RCE Flaws as Embargoed Details Leak
DHS Orders Federal Civilian Agencies to Remove DeepSeek Products
Feds Suspect Ransom Negotiator Helped Run ShinyHunters Leak Site
23andMe Successor Settles With California for $6M Over Breach
ICO Reprimands Welsh Bodies After ‘Password1’ Account Breach
Mozilla, Google, Apple Block Eight Weak eMudhra CA Keys
Hacker Claims NBCUniversal Production and Tax-Credit Data Theft
Hijacked Account Plants Stealer in Five OVHcloud CLI Releases
CISA, FBI Say SafePay Ransomware Has Hit 600+ Organizations
Public Exploit Released for Critical FortiSIEM Flaw CVE-2026-106173
State Bank of India Confirms Data Leak of 3,897 Customer Records
Conduent Agrees to $80M Settlement Over Breach of 62M People
Public Exploit Chains 37-Year-Old BSD Bug for OpenBSD Root
OpenCode Silently Patched Critical RCE Flaw With No CVE
Qilin, INC Ransomware Exploit PAN-OS Flaw, Then Pivot to VMware
TeamUpdraft Breach Lets Attackers Backdoor WordPress Sites
Siemens Software Center Flaw Exploited in ROMULUS ClickFix Attacks
Laravel TokenGuard Flaw Lets Attackers Log In as Any User
Roundcube 1.6.20 and 1.7.5 Fix 20 Flaws, Including IMAP Injection
Citizen Lab Confirms Pegasus on Belgrade Rector’s Phone Before Vote
AIA0001 Hacker Uses AI Agents to Breach 100+ Company Websites
Parkview Health Disables Network After Suspicious Activity
Plex2Shell Exploit Chain Hits Plex Servers a Day After PoC Release
Microsoft Confirms Windows Update Breaks Exchange Sign-In, Mail Flow
OpenCode Console Breach May Have Exposed Saved AI Provider API Keys
ConnectWise Cloud Backup Stays Offline After 173 Tenants Hit
Aeroflot Flights Canceled After Hacktivist Cyberattack Cripples Airline Systems
News
Aeroflot Flights Canceled After Hacktivist Cyberattack Cripples Airline Systems
Aeroflot’s operations were disrupted after a cyberattack claimed by Ukrainian and Belarusian hacktivists who allege wiping critical systems and exfiltrating sensitive airline data.
Orange Discloses Cyberattack, Service Disruptions in France Following Breach
News
Orange Discloses Cyberattack, Service Disruptions in France Following Breach
French telecom giant Orange confirmed a cyberattack that disrupted services in France. The affected system was isolated; no data exfiltration has been found yet.
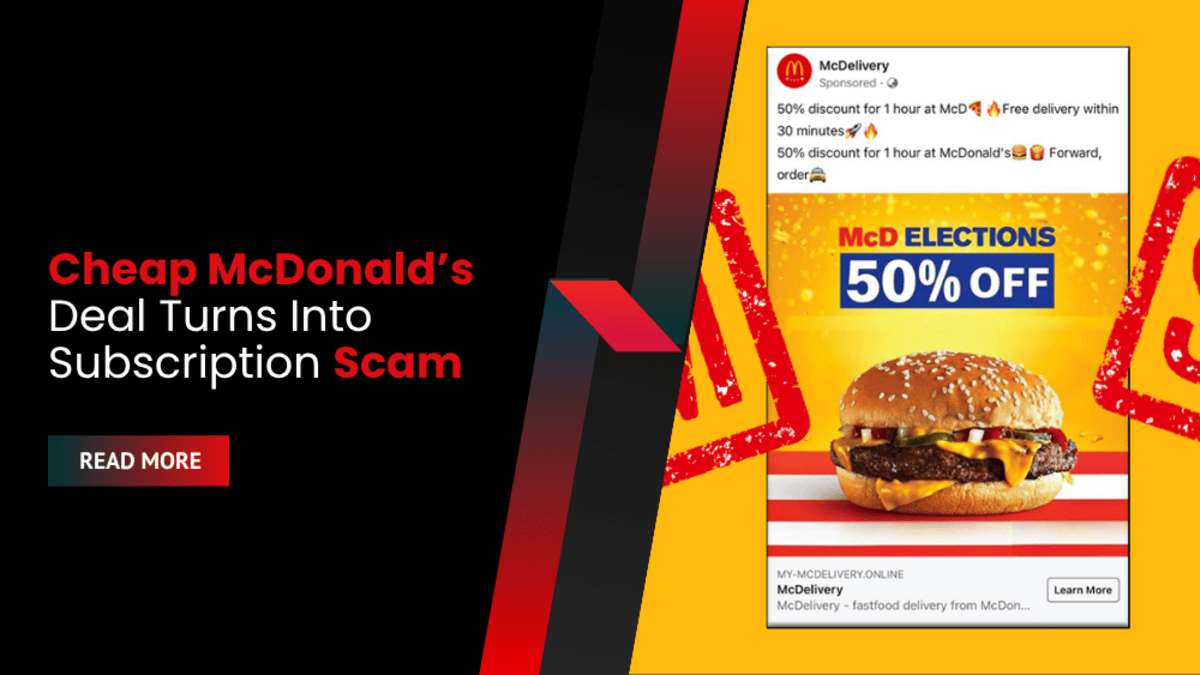
Cheap McDonald’s Deal Turns Into Subscription Scam: Over 10,000 Romanians Targeted via Facebook and Instagram Ads
News
Cheap McDonald’s Deal Turns Into Subscription Scam: Over 10,000 Romanians Targeted via Facebook and Instagram Ads
A $2 McDonald's deal scam has duped over 10,000 Romanians into €63.42 bi-weekly subscriptions via fake ads on Instagram and Facebook, Bitdefender reports.
Scattered Spider Ransomware Group Ramps Up Sophisticated Attacks Targeting Enterprises Globally
Cybersecurity
Scattered Spider Ransomware Group Ramps Up Sophisticated Attacks Targeting Enterprises Globally
The U.S. Cybersecurity and Infrastructure Security Agency (CISA), along with the FBI and international partners, has issued an updated advisory ...
Lynx Ransomware: INC Ransomware Reincarnated
Resources
Lynx Ransomware: INC Ransomware Reincarnated
The Lynx ransomware group is a financially motivated threat actor operating under a Ransomware-as-a-Service (RaaS) model. Emerging as a successor to the INC ransomware group ...
How to Backup and Restore the Windows Registry
Blog
How to Backup and Restore the Windows Registry
Protect your system settings from accidental changes or corruption. Learn how to safely backup and restore the Windows Registry with this easy step-by-step guide.
Google Patches Gemini CLI Vulnerability That Enabled Silent Code Execution and Data Theft
News
Google Patches Gemini CLI Vulnerability That Enabled Silent Code Execution and Data Theft
A critical flaw in Google’s Gemini CLI exposed developers to silent command execution and data theft through poisoned context files, prompting an urgent security patch. ...
Tea App Data Breach Deepens as 1.1 Million Private Messages Are Exposed
News
Tea App Data Breach Deepens as 1.1 Million Private Messages Are Exposed
Tea app’s data breach escalates as 1.1 million private messages and 72,000 sensitive images, including government IDs and selfies, are leaked on hacker forums.
NASCAR Confirms Data Breach Tied to Medusa Ransomware Gang, SSNs Exposed
News
NASCAR Confirms Data Breach Tied to Medusa Ransomware Gang, SSNs Exposed
NASCAR confirms a data breach exposing Social Security numbers, linked to Medusa ransomware gang. Victims are receiving breach notifications and one year of credit monitoring. ...
Hackers Claim Deep Access to Systems, Threaten to Leak Passenger Data
News
Hackers Claim Deep Access to Systems, Threaten to Leak Passenger Data
Aeroflot suffers massive cyberattack by pro-Ukraine hackers, disrupting flights, destroying 7,000 servers, and exposing personal data of passengers and staff. A criminal probe is underway. ...
CISA Warns of Ongoing Exploits Targeting PaperCut RCE Vulnerability, Urges Immediate Patching
News
CISA Warns of Ongoing Exploits Targeting PaperCut RCE Vulnerability, Urges Immediate Patching
CISA warns that hackers are actively exploiting a PaperCut vulnerability (CVE-2023-2533) for remote code execution, urging organizations to patch systems immediately to reduce risk.
Exploit Published for Actively Exploited Cisco ISE Vulnerability Leading to Root Access
News
Exploit Published for Actively Exploited Cisco ISE Vulnerability Leading to Root Access
Cisco ISE vulnerability CVE-2025-20281 now has a public exploit, enabling remote root access. Active exploitation is confirmed. Patching remains the only defense.
BlackSuit Ransomware Operation Disrupted in Global Law Enforcement Seizure
News
BlackSuit Ransomware Operation Disrupted in Global Law Enforcement Seizure
Authorities have seized the BlackSuit ransomware gang’s dark web site, disrupting its operations as members appear to rebrand under a new name: Chaos ransomware.
Scattered Spider Ramps Up VMware ESXi Attacks Targeting U.S. Enterprise Virtual Infrastructure
News
Scattered Spider Ramps Up VMware ESXi Attacks Targeting U.S. Enterprise Virtual Infrastructure
Scattered Spider hackers are compromising VMware ESXi infrastructure through social engineering, enabling full control and ransomware deployment without exploiting any software vulnerabilities.
Allianz Life Data Breach Exposes Information of Over 1 Million Customers
News
Allianz Life Data Breach Exposes Information of Over 1 Million Customers
A recent data breach at Allianz Life compromised personal data of most of its 1.4 million customers via a third-party CRM system, possibly tied to ...
Amazon Q Developer Extension Compromised to Include Data-Wiping Commands
News
Amazon Q Developer Extension Compromised to Include Data-Wiping Commands
A hacker breached Amazon's AI coding assistant for Visual Studio Code, injecting data-wiping instructions before detection. A patched version was released following security reports.
Philadelphia Insurance Companies Reports Personal Data Breach After June Cyber Incident
News
Philadelphia Insurance Companies Reports Personal Data Breach After June Cyber Incident
Philadelphia Insurance Companies has confirmed a personal data breach involving driver’s license numbers and birth dates following a June cyberattack that disrupted multiple insurers.
Fog Ransomware: Data in the Mist
Resources
Fog Ransomware: Data in the Mist
Fog ransomware, a prolific and secretive threat actor, targets organizations globally, deploying sophisticated multi-stage attacks resulting in data encryption and exfiltration. Victims span various sectors. ...
Chinese Espionage Groups Target SharePoint Servers in Large-Scale Exploitation Campaigns
News
Chinese Espionage Groups Target SharePoint Servers in Large-Scale Exploitation Campaigns
Microsoft links SharePoint attacks to three Chinese espionage groups, urging immediate patching as critical vulnerabilities enable full server compromise without authentication.
Interlock Ransomware Escalates Attacks on North America and Europe, Warns CISA
News
Interlock Ransomware Escalates Attacks on North America and Europe, Warns CISA
CISA and FBI warn that Interlock ransomware is accelerating attacks across North America and Europe, targeting healthcare and critical infrastructure with advanced RATs and extortion ...

Application Security
LiteLLM 1.107.0 Backdoored in PyPI Supply Chain Attack

Cybersecurity
WhiteArmour Claims Breach of Disney Staff Directory

Cybersecurity
Exposed Servers Reveal INC and Gentlemen Ransomware AI Operations
Cybersecurity
CISA, FBI Say SafePay Ransomware Has Hit 600+ Organizations

TOP CYBERSECURITY HEADLINES

This Week’s Security Spotlight

Application Security
PHP Ships Emergency Patches for PHP2Shell as Exploitation Begins

Cybersecurity
CISA, FBI Say SafePay Ransomware Has Hit 600+ Organizations
Cybersecurity
Conduent Agrees to $80M Settlement Over Breach of 62M People
Application Security
Siemens Software Center Flaw Exploited in ROMULUS ClickFix Attacks

Trending

Daily Briefing Newsletter

Subscribe to the Daily Security Review Email Briefing to stay informed on the latest threats, trends, and technology, along with insightful columns from industry experts.

Featured Videos​

  • All
  • Application Security
  • Blog
  • CVE Vulnerability Alerts
  • Cybersecurity
  • Cybersecurity Newsletter
  • Data Security
  • Endpoint Security
  • Identity and Access Management
  • Information Security
  • Network Security
  • News
  • Phishing
  • Podcasts
  • Product Reviews
  • Ransomware
  • Ransomware Victims
  • Resources
  • Security Spotlight
  • Sponsored
  • Threat Actors
  • Threat Actors
  • Threat Detection Tools
Norway Attributes Dam Cyberattack to Russian Hackers
Norway confirmed that Russian state-sponsored hackers breached the Bremanger dam’s control systems in April 2025, releasing 1.9 million gallons of water. While no damage occurred, ...
Chrome Extension FreeVPN One Secretly Captures Screens
Security researchers found that FreeVPN.One, a Chrome extension with over 100,000 installs and a verified badge, secretly captured user screenshots, URLs, and device data. Updates ...
Critical PostgreSQL Flaws Allow Code Injection During Database Restoration
The PostgreSQL team has disclosed three critical vulnerabilities—CVE-2025-8714, CVE-2025-8715, and CVE-2025-1094—impacting backup and restore utilities. These flaws enable malicious code injection and SQL exploitation, posing ...
Internet Archive Abused to Host Stealthy Malware JScript Loaders
Attackers are abusing the Internet Archive to host obfuscated malware loaders, launching multi-stage infection chains that deliver the Remcos RAT. By exploiting trusted infrastructure, threat ...
Business Council of New York State Data Breach: Personal Health Data of 47,000 People Exposed
BCNYS reports a two-day February intrusion discovered in August exposed personal, financial, and health data for 47,329 people, prompting rolling notifications and credit monitoring for ...
Clickjacking Vulnerability Exposes Autofill Data Across Major Extensions
Attackers use ADFS redirect phishing through legitimate office.com links, bypassing URL filters and MFA, to steal Microsoft 365 logins via malvertising and conditional access tricks.
Financial App Data Leak in Turkey Puts Millions at Risk
An unprotected MongoDB tied to FinansCepte and FinansWebde exposed over four million records, putting Turkish users at risk of phishing, credential stuffing, and manipulated financial ...
GenAI Powers Harder-to-Detect Phishing Threats
New research from Unit 42 shows adversaries are combining AI website builders, writing assistants, deepfakes, and chatbots to automate large-scale campaigns that closely mimic trusted ...
PyPI Cracks Down on Domain Expiration Attacks to Protect Python Packages
The Python Package Index (PyPI), the backbone of the global Python ecosystem, has rolled out new security safeguards aimed at stopping a dangerous form of ...
AI Joins the Fight Against Exploits: Google and Mozilla Patch Dangerous Vulnerabilities
Both Google and Mozilla have rolled out urgent security updates to patch multiple high-severity vulnerabilities in their flagship browsers—Google Chrome and Mozilla Firefox—underscoring the constant ...
Britain Backs Down: UK Drops Encryption Backdoor Demand on Apple
A major international clash over encryption has come to a dramatic resolution. Earlier this year, the U.K. government, acting under its controversial Investigatory Powers Act ...
PipeMagic Backdoor: How Ransomware Actors Exploited a Windows Zero-Day
In early 2025, Microsoft and security researchers uncovered PipeMagic, a modular and memory-resident backdoor that has been quietly leveraged in ransomware campaigns worldwide. Disguised as ...
270,000 Intel Employee Records at Risk from Authentication Bypass and Hardcoded Credentials
In late 2024, Intel faced a major cybersecurity wake-up call when security researcher Eaton Zveare uncovered a series of vulnerabilities inside the company’s internal systems—flaws ...
LG Hai Phong Earns CSMS Level 3 Certification at Its Largest Vehicle Component Base
LG’s Hai Phong plant earned CSMS Level 3 Certification from TÜV Rheinland, the first facility to hold both Level 2 and Level 3 simultaneously, validating ...
XenoRAT Malware Campaign Targets Embassies in South Korea
A multi-stage espionage campaign using XenoRAT malware has targeted foreign embassies in South Korea, with evidence linking the activity to both North Korean and Chinese ...
SentinelOne Expands Partnership With Mimecast to Advance People-Focused Cybersecurity
SentinelOne and Mimecast deepen integration, pairing Singularity endpoint telemetry with Human Risk Management to prioritize people-focused cybersecurity and reduce human-caused breaches.
Inotiv Ransomware Attack Disrupts Operations After Qilin Claims 176GB Data Theft
Inotiv confirms a ransomware attack encrypted systems and data, disrupting operations. SEC filing cites Qilin claims of 176GB theft as investigators restore and assess impact.
Researcher Harvests 270k Employee Records Exploiting Intel Flaw
Researcher Eaton Zveare found four flaws that exposed 270,000 Intel employee records via unauthenticated APIs and hardcoded credentials, then received only an automated “Thank You ...
How Social Engineering and Vendor Weaknesses Led to Allianz Life’s Massive Breach
In July 2025, Allianz Life Insurance Company of North America confirmed a data breach impacting over 1.1 million customers, financial professionals, and employees—a stark reminder ...
Cloud Computing Heist: $3.5 Million Fraud Leads to Prison for Fake Crypto Influencer
The U.S. Department of Justice has closed the chapter on one of the most audacious cloud fraud and cryptojacking schemes in recent years. Charles O. ...