Cyber Security
DOJ Seizes $1.2B of North Korea’s Binance Haul, Disrupts FaceStealer
TSMC Confirms Employee Data Leak Traced to Third-Party Cloud Vendor
Citrix Patches 28 NetScaler Flaws and Critical Console Auth Bypass
Apify Rotates API Tokens and Urges 2FA Resets After Breach
PostgreSQL Fixes 52 Vulnerabilities and Ends Support for Version 14
PTC Patches Critical Windchill and FlexPLM Flaw CVE-2026-126325
Zoho Publishes Eight Critical ManageEngine CVEs, One Rated 9.9
Mitel Fixes Critical MiVoice MX-ONE Authentication Bypass Flaw
Google Cloud Warns of AMD Turin CPU Flaws Leaking Data in VMs
Red Hat Publishes 21 CVEs, Led by CVSS 9.6 Satellite Sandbox Bypass
School Bomb-Threat Emails Trace to Addresses in Stolen Credential Data
Maersk Confirms Data Theft as WhiteArmor Demands $5 Million
Attackers Hijack ScreenConnect at MSPs as ConnectWise Cuts Extensions
wfx-loot Campaign Used 4,837 Hijacked GitHub Accounts for CI Stealer
Apache 2.4.71 Fixes Critical mod_http2 RCE Flaw CVE-2026-119618
Critical MongoDB Flaw CVE-2026-118383 Crashes Replica Set Members
Node.js Security Releases Fix HTTP/2 Crash and TLS Memory Leaks
Poland Takes ePUAP E-Government Platform Offline After Cyberattack
AntiFox AI Pentest Platform Abused to Steal AWS Production Secrets
Researchers Unmask Qilin Ransomware Administrator ‘Haise’
Critical Red Hat Quay Flaw CVE-2026-123710 Allows Signing Takeover
Zoom Patches Critical Workplace for Windows Flaw CVE-2026-108187
Chrome 157 Update Fixes 83 Flaws, Including Five Critical Bugs
Telegram Patches Android Remote Code Execution Bug After V12 Demo
Public Exploit Released for Linux Kernel AF_UNIX Flaw CVE-2026-80521
Over 35,000 Grok-Built Apps Found Open Online, Some Leaking Data
Microsoft Patches Outlook Zero-Day CVE-2026-124194 in 1,000+ Fixes
SAP Patches Four CVSS 10.0 Flaws Including ICM2SHELL RCE
Xen Orchestra Auth Bypass Exploited to Hijack XCP-ng Hosts
Barracuda Flaws CVE-2026-116606 and CVE-2026-111560 Exploited
Qilin Ransomware Claims Asefa Attack: 210GB of Data Leaked Including FC Barcelona Insurance Files
News
Qilin Ransomware Claims Asefa Attack: 210GB of Data Leaked Including FC Barcelona Insurance Files
Qilin ransomware group claims to have stolen 210GB of sensitive data from Spanish insurer Asefa, including internal documents and a Camp Nou insurance plan.
Spyware Scandal Expands as Second Italian Journalist Targeted with Paragon Surveillance Tool
News
Spyware Scandal Expands as Second Italian Journalist Targeted with Paragon Surveillance Tool
Citizen Lab confirms Paragon spyware targeted a second journalist at Fanpage, deepening Italy’s political surveillance controversy and raising new concerns over investigative oversight.
How to Defend Your Organization Against Scattered Spider’s Service Desk Attacks
Application Security
How to Defend Your Organization Against Scattered Spider’s Service Desk Attacks
Scattered Spider service desk attacks exploit social engineering to bypass security, targeting help desks for credential access. Learn defense strategies using open-source tools and training. ...
Food Delivery App GonnaOrder Leaked Customer Names, Addresses, and Order Info for Nearly Two Years
News
Food Delivery App GonnaOrder Leaked Customer Names, Addresses, and Order Info for Nearly Two Years
A misconfigured Kafka Broker on GonnaOrder’s platform exposed customer names, phone numbers, and delivery details across Europe from August 2022 to May 2025.
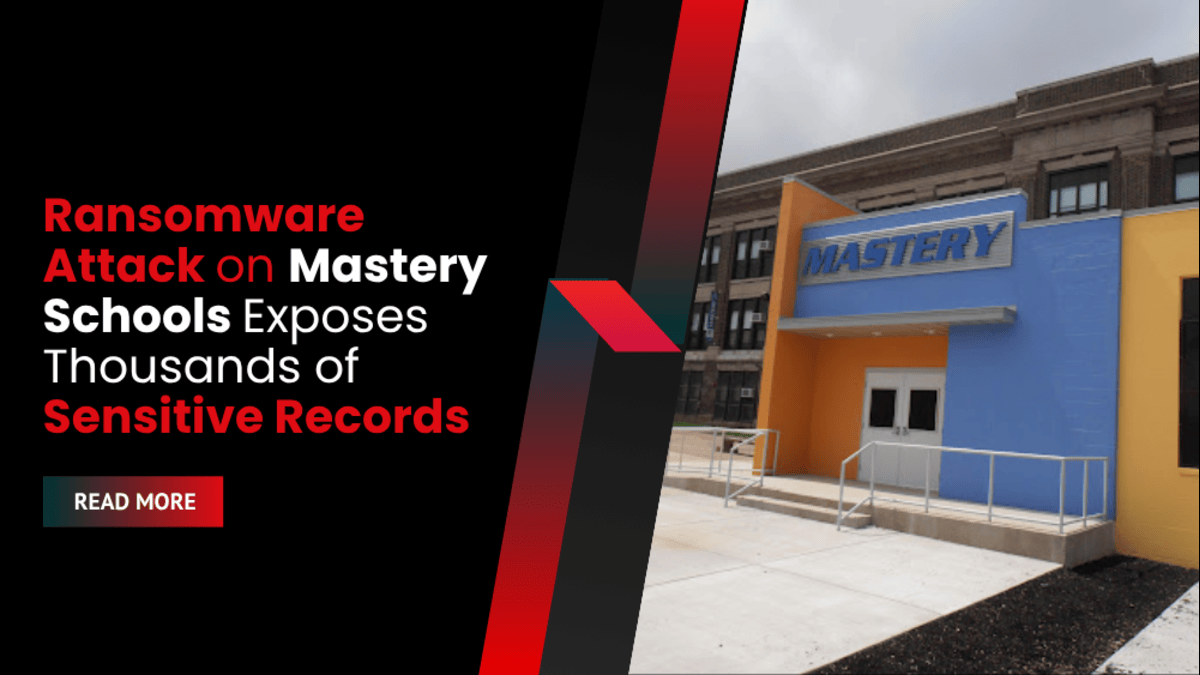
Ransomware Attack on Mastery Schools Exposes Thousands of Sensitive Records, Including Credit Card and Biometric Data
News
Ransomware Attack on Mastery Schools Exposes Thousands of Sensitive Records, Including Credit Card and Biometric Data
A ransomware breach at Mastery Schools in Philadelphia exposed sensitive personal and financial records, affecting over 37,000 individuals including students, staff, and families.
Headero App Data Leak Exposes Over Four Million Sensitive User Records, Including GPS and Sexual Preferences
News
Headero App Data Leak Exposes Over Four Million Sensitive User Records, Including GPS and Sexual Preferences
A misconfigured database tied to the Headero dating app exposed over four million sensitive user records, including GPS coordinates, explicit chat logs, and STD statuses. ...
Erie Insurance Cyberattack Causes System-Wide Disruptions and Portal Outages
News
Erie Insurance Cyberattack Causes System-Wide Disruptions and Portal Outages
Erie Insurance confirms a cyberattack as the source of major service disruptions since June 7, affecting customer access, claims processing, and business operations.
Mental Health Provider Mount Rogers Targeted by INC Ransom, Internal Documents and Personal Details Leaked
News
Mental Health Provider Mount Rogers Targeted by INC Ransom, Internal Documents and Personal Details Leaked
Ransomware group INC Ransom breached Mount Rogers Community Services, leaking internal files, personal emails, and invoices from the mental health provider's systems.
BlackSuit (Royal) Ransomware: Conti Ransomware Reborn
Resources
BlackSuit (Royal) Ransomware: Conti Ransomware Reborn
BlackSuit, formerly Royal, is a sophisticated ransomware group using multi-vector attacks, partial encryption, and double extortion to target global organizations, including critical infrastructure. Their operations ...
Texas Dept. of Transportation Breach Exposes 300,000 Crash Records in May 2025
News
Texas Dept. of Transportation Breach Exposes 300,000 Crash Records in May 2025
TxDOT suffered a breach on May 12, 2025, leaking 300,000 crash reports. Stolen data includes driver’s license numbers, insurance info, and crash details.
Ivanti Workspace Control Exposes SQL Credentials Through Hardcoded Key Flaws
Endpoint Security
Ivanti Workspace Control Exposes SQL Credentials Through Hardcoded Key Flaws
Ivanti patched three high-severity vulnerabilities in Workspace Control caused by hardcoded cryptographic keys, which exposed SQL and environment credentials to local authenticated attackers.
Mirai Botnet Exploits Wazuh Servers via Remote Code Execution Vulnerability
News
Mirai Botnet Exploits Wazuh Servers via Remote Code Execution Vulnerability
A critical RCE flaw in Wazuh servers is being exploited by Mirai botnet variants, allowing attackers to execute Python code through malicious API requests.
FIN6 Hackers Target Recruiters with Fake Job Seekers and Malware-Loaded Resumes
News
FIN6 Hackers Target Recruiters with Fake Job Seekers and Malware-Loaded Resumes
FIN6 hackers are impersonating job seekers to infiltrate recruiter systems, delivering the More_Eggs malware via AWS-hosted resume sites and phishing tactics on LinkedIn and Indeed. ...
4,000+ Fake Sites Used in Scam Marketplace Ads on Facebook to Impersonate Top Retail Brands
News
4,000+ Fake Sites Used in Scam Marketplace Ads on Facebook to Impersonate Top Retail Brands
A scam network using over 4,000 fake websites is impersonating Amazon, Birkenstock, and more, pushing fraudulent Facebook Marketplace ads and stealing user data.
Bert Ransomware Group Claims Data Theft from Global Port Agency S5
News
Bert Ransomware Group Claims Data Theft from Global Port Agency S5
Ransomware gang Bert claims to have stolen 140GB of sensitive data from S5 Agency World, a maritime logistics firm with operations in 360+ ports globally. ...
INC Ransom: Master of Double Extortion
Ransomware
INC Ransomware: Master of Double Extortion
INC Ransomware is a sophisticated and relatively new cybercriminal group known for its targeted ransomware attacks against corporate and organizational networks. They exhibit a high ...
Ticketmaster Data from Snowflake Attack Appears Briefly on Arkana Security Extortion Site
News
Ticketmaster Data from Snowflake Attack Appears Briefly on Arkana Security Extortion Site
Old Ticketmaster data stolen in the 2024 Snowflake attack was briefly relisted for sale by Arkana Security, sparking confusion over a possible new breach.
Ransomware Attack on Sensata Technologies Leads to Data Breach Impacting Employee Information
News
Ransomware Attack on Sensata Technologies Leads to Data Breach Impacting Employee Information
Sensata Technologies confirms employee data was stolen in a ransomware breach that impacted operations and exposed sensitive personal and financial details from current and former ...
United Natural Foods Cyberattack Disrupts Operations Across North America
News
United Natural Foods Cyberattack Disrupts Operations Across North America
United Natural Foods, a key supplier to Whole Foods, suffered a cyberattack that disrupted customer orders and forced systems offline as investigations and recovery efforts ...
Over 84,000 Roundcube Webmail Servers Exposed to Actively Exploited Remote Code Flaw
News
Over 84,000 Roundcube Webmail Servers Exposed to Actively Exploited Remote Code Flaw
Over 84,000 Roundcube webmail servers remain exposed to a critical RCE flaw (CVE-2025-49113) despite a June 2025 patch fixing the vulnerability.

CVE Vulnerability Alerts
PHP2Shell Attacks on Check Point Gateways Deploy TSGA, ESXi Wiper

Cybersecurity
Maersk Confirms Data Theft as WhiteArmor Demands $5 Million
Cybersecurity
Researchers Unmask Qilin Ransomware Administrator ‘Haise’

TOP CYBERSECURITY HEADLINES

This Week’s Security Spotlight

Cybersecurity
DOJ Seizes $1.2B of North Korea’s Binance Haul, Disrupts FaceStealer
Cybersecurity
Researchers Unmask Qilin Ransomware Administrator ‘Haise’
CVE Vulnerability Alerts
Barracuda Flaws CVE-2026-116606 and CVE-2026-111560 Exploited

CVE Vulnerability Alerts
Intel and AMD Patch Over 200 Vulnerabilities in November Updates

Trending

Daily Briefing Newsletter

Subscribe to the Daily Security Review Email Briefing to stay informed on the latest threats, trends, and technology, along with insightful columns from industry experts.

Featured Videos​

Podcasts

Sorry, we couldn't find any posts. Please try a different search.

  • All
  • AI Security
  • Application Security
  • Blog
  • CVE Vulnerability Alerts
  • Cybersecurity
  • Cybersecurity Newsletter
  • Data Security
  • Endpoint Security
  • Identity and Access Management
  • Information Security
  • Network Security
  • News
  • Phishing
  • Podcasts
  • Product Reviews
  • Ransomware
  • Ransomware Victims
  • Resources
  • Security Spotlight
  • Sponsored
  • Threat Actors
  • Threat Actors
  • Threat Detection Tools
Aeroflot in Chaos: How Hackers Crippled Russia’s Flagship Airline
On July 28, 2025, Aeroflot—Russia’s largest state-owned airline—was brought to its knees in one of the most severe cyberattacks since the country’s invasion of Ukraine ...
Lynx Ransomware: INC Ransomware Reincarnated
The Lynx ransomware group is a financially motivated threat actor operating under a Ransomware-as-a-Service (RaaS) model. Emerging as a successor to the INC ransomware group ...
How to Backup and Restore the Windows Registry
Protect your system settings from accidental changes or corruption. Learn how to safely backup and restore the Windows Registry with this easy step-by-step guide.
Google Patches Gemini CLI Vulnerability That Enabled Silent Code Execution and Data Theft
A critical flaw in Google’s Gemini CLI exposed developers to silent command execution and data theft through poisoned context files, prompting an urgent security patch. ...
NASCAR Confirms Data Breach Tied to Medusa Ransomware Gang, SSNs Exposed
NASCAR confirms a data breach exposing Social Security numbers, linked to Medusa ransomware gang. Victims are receiving breach notifications and one year of credit monitoring. ...
Tea App Data Breach Deepens as 1.1 Million Private Messages Are Exposed
Tea app’s data breach escalates as 1.1 million private messages and 72,000 sensitive images, including government IDs and selfies, are leaked on hacker forums.
Hackers Claim Deep Access to Systems, Threaten to Leak Passenger Data
Aeroflot suffers massive cyberattack by pro-Ukraine hackers, disrupting flights, destroying 7,000 servers, and exposing personal data of passengers and staff. A criminal probe is underway. ...
CISA Warns of Ongoing Exploits Targeting PaperCut RCE Vulnerability, Urges Immediate Patching
CISA warns that hackers are actively exploiting a PaperCut vulnerability (CVE-2023-2533) for remote code execution, urging organizations to patch systems immediately to reduce risk.
Exploit Published for Actively Exploited Cisco ISE Vulnerability Leading to Root Access
Cisco ISE vulnerability CVE-2025-20281 now has a public exploit, enabling remote root access. Active exploitation is confirmed. Patching remains the only defense.
Neferpitou Claims Cyberattack on French Naval Defense Giant
French defense contractor Naval Group, a cornerstone of Europe’s naval defense industry, is facing a high-stakes cybersecurity crisis. A threat actor known as “Neferpitou” claims ...
Root Evidence Launches With $12.5M to Redefine Vulnerability Management
In July 2025, a team of seasoned cybersecurity leaders launched Root Evidence, a Boise-based startup with a mission to revolutionize how organizations tackle vulnerability management. ...
NASCAR Hit by Medusa Ransomware: 1TB of Data Stolen in April 2025 Cyberattack
In April 2025, NASCAR became the latest victim of a major cyberattack, with hackers infiltrating its network between March 31 and April 3. During the ...
Scattered Spider Strikes Again: Inside the VMware ESXi Ransomware Tactics
In this episode, we examine the sophisticated operations of Scattered Spider—also known as Muddled Libra, UNC3944, and Octo Tempest—a financially motivated cybercriminal group that has ...
BlackSuit Ransomware Operation Disrupted in Global Law Enforcement Seizure
Authorities have seized the BlackSuit ransomware gang’s dark web site, disrupting its operations as members appear to rebrand under a new name: Chaos ransomware.
Scattered Spider Ramps Up VMware ESXi Attacks Targeting U.S. Enterprise Virtual Infrastructure
Scattered Spider hackers are compromising VMware ESXi infrastructure through social engineering, enabling full control and ransomware deployment without exploiting any software vulnerabilities.
Amazon Q Developer Extension Compromised to Include Data-Wiping Commands
A hacker breached Amazon's AI coding assistant for Visual Studio Code, injecting data-wiping instructions before detection. A patched version was released following security reports.
Allianz Life Data Breach Exposes Information of Over 1 Million Customers
A recent data breach at Allianz Life compromised personal data of most of its 1.4 million customers via a third-party CRM system, possibly tied to ...
Philadelphia Insurance Companies Reports Personal Data Breach After June Cyber Incident
Philadelphia Insurance Companies has confirmed a personal data breach involving driver’s license numbers and birth dates following a June cyberattack that disrupted multiple insurers.
Koske Malware Hides in Panda Images, Weaponizes AI to Target Linux
A new and highly sophisticated malware strain named Koske is redefining the threat landscape for Linux environments. Suspected to be partially developed using artificial intelligence, ...
Operation Checkmate: BlackSuit Ransomware’s Dark Web Sites Seized
BlackSuit, the ransomware strain known for crippling critical sectors and demanding multi-million dollar payouts, has just suffered a devastating blow. In a coordinated international law ...