Cyber Security
DOJ Seizes $1.2B of North Korea’s Binance Haul, Disrupts FaceStealer
TSMC Confirms Employee Data Leak Traced to Third-Party Cloud Vendor
Citrix Patches 28 NetScaler Flaws and Critical Console Auth Bypass
Apify Rotates API Tokens and Urges 2FA Resets After Breach
PostgreSQL Fixes 52 Vulnerabilities and Ends Support for Version 14
PTC Patches Critical Windchill and FlexPLM Flaw CVE-2026-126325
Zoho Publishes Eight Critical ManageEngine CVEs, One Rated 9.9
Mitel Fixes Critical MiVoice MX-ONE Authentication Bypass Flaw
Google Cloud Warns of AMD Turin CPU Flaws Leaking Data in VMs
Red Hat Publishes 21 CVEs, Led by CVSS 9.6 Satellite Sandbox Bypass
School Bomb-Threat Emails Trace to Addresses in Stolen Credential Data
Maersk Confirms Data Theft as WhiteArmor Demands $5 Million
Attackers Hijack ScreenConnect at MSPs as ConnectWise Cuts Extensions
wfx-loot Campaign Used 4,837 Hijacked GitHub Accounts for CI Stealer
Apache 2.4.71 Fixes Critical mod_http2 RCE Flaw CVE-2026-119618
Critical MongoDB Flaw CVE-2026-118383 Crashes Replica Set Members
Node.js Security Releases Fix HTTP/2 Crash and TLS Memory Leaks
Poland Takes ePUAP E-Government Platform Offline After Cyberattack
AntiFox AI Pentest Platform Abused to Steal AWS Production Secrets
Researchers Unmask Qilin Ransomware Administrator ‘Haise’
Critical Red Hat Quay Flaw CVE-2026-123710 Allows Signing Takeover
Zoom Patches Critical Workplace for Windows Flaw CVE-2026-108187
Chrome 157 Update Fixes 83 Flaws, Including Five Critical Bugs
Telegram Patches Android Remote Code Execution Bug After V12 Demo
Public Exploit Released for Linux Kernel AF_UNIX Flaw CVE-2026-80521
Over 35,000 Grok-Built Apps Found Open Online, Some Leaking Data
Microsoft Patches Outlook Zero-Day CVE-2026-124194 in 1,000+ Fixes
SAP Patches Four CVSS 10.0 Flaws Including ICM2SHELL RCE
Xen Orchestra Auth Bypass Exploited to Hijack XCP-ng Hosts
Barracuda Flaws CVE-2026-116606 and CVE-2026-111560 Exploited
Russian Market Becomes Leading Hub for Stolen Credentials from Info-Stealer Malware
News
Russian Market Becomes Leading Hub for Stolen Credentials from Info-Stealer Malware
The Russian Market has surged in popularity as a major cybercrime marketplace, offering stolen credentials harvested by info-stealer malware like Lumma and Acreed.
Kaiser Permanente Recovers from Widespread Network Outage That Disrupted Patient Services Nationwide
News
Kaiser Permanente Recovers from Widespread Network Outage That Disrupted Patient Services Nationwide
Kaiser Permanente suffered a major network outage that disrupted electronic health records and patient services across the U.S. System functionality was restored the following day. ...
Remote Code Execution Flaw in vBulletin Forum Software Under Active Exploitation
News
Remote Code Execution Flaw in vBulletin Forum Software Under Active Exploitation
Two critical vBulletin vulnerabilities, actively exploited in the wild, allow attackers to execute code remotely by abusing template logic and PHP’s Reflection API.
Cisco IOS XE Wireless LAN Controller Vulnerability Exposes Enterprises to Remote Code Execution Risks
News
Cisco IOS XE Wireless LAN Controller Vulnerability Exposes Enterprises to Remote Code Execution Risks
Exploit details for a critical Cisco IOS XE Wireless LAN Controller vulnerability (CVE-2025-20188) are now public, raising urgent concerns about remote code execution risks.
Germany Identifies TrickBot and Conti Ransomware Ringleader as Vitaly Kovalev
News
Germany Identifies TrickBot and Conti Ransomware Ringleader as Vitaly Kovalev
Germany has named Vitaly Kovalev, aka "Stern," as the leader of the Conti ransomware and TrickBot gangs in a major breakthrough tied to Operation Endgame. ...
Latrodectus Malware Infected Over 44,000 IPs Before Operation Endgame Takedown
News
Latrodectus Malware Infected Over 44,000 IPs Before Operation Endgame Takedown
Latrodectus malware infected over 44,000 IP addresses before Operation Endgame's global takedown, with Shadowserver warning of critical ongoing threats across infected systems.
184 Million Login Credentials Exposed in Major Unprotected Database Leak
News
184 Million Login Credentials Exposed in Major Unprotected Database Leak
Over 184 million login credentials were exposed online in plain text, revealing widespread negligence in data protection and the growing threat of credential-based cyberattacks.
This Week In Cybersecurity: 26th to 30th May, 2025
Cybersecurity Newsletter
This Week In Cybersecurity: 26th to 30th May, 2025
"Cybersecurity threats escalate as ransomware attacks target major organizations, exposing sensitive data and highlighting vulnerabilities in systems across various industries. Stay informed."
Victoria’s Secret Takes Website Offline Following Security Incident
News
Victoria’s Secret Takes Website Offline Following Security Incident
Victoria’s Secret temporarily disabled its website and limited in-store services to address a cybersecurity incident. Third-party experts have been engaged; stores remain open.
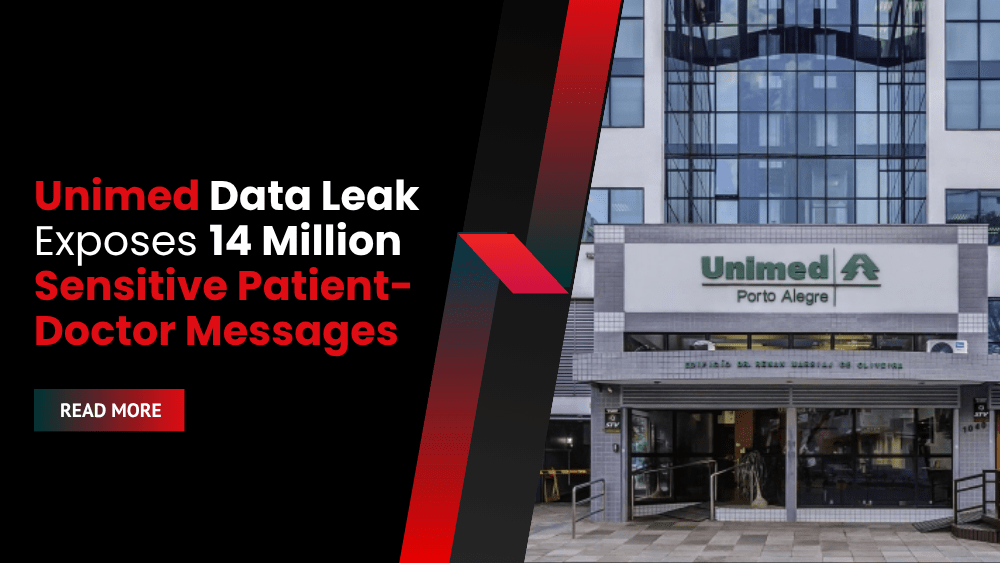
Unimed Data Leak Exposes 14 Million Sensitive Patient-Doctor Messages
News
Unimed Data Leak Exposes 14 Million Sensitive Patient-Doctor Messages
An exposed Unimed server leaked over 14 million private patient-doctor messages, including medical data, documents, and IDs—posing major cybersecurity and privacy risks.
Russian Nuclear Facility Blueprints Exposed in Massive Security Breach
News
Russian Nuclear Facility Blueprints Exposed in Massive Security Breach
Russian nuclear facility blueprints were exposed in a public procurement database, revealing sensitive layouts of missile silos and bunkers tied to Moscow’s nuclear modernization.
APT41 Exploits Google Calendar for Stealth Malware Control and Data Theft
News
APT41 Exploits Google Calendar for Stealth Malware Control and Data Theft
Chinese APT41 hackers used Google Calendar to run malware operations and exfiltrate data, exploiting Calendar events for covert command-and-control and stealth communications.
RE/MAX Targeted by Medusa Ransomware in Alleged 150GB Data Breach
News
RE/MAX Targeted by Medusa Ransomware in Alleged 150GB Data Breach
Medusa ransomware claims a 150GB data breach at RE/MAX and demands $200K ransom. Exposed files include agent details, commissions, and internal property documents.
German Cybersecurity Agency Flags Critical Windows Server 2025 Flaw Enabling Domain Takeover
News
German Cybersecurity Agency Flags Critical Windows Server 2025 Flaw Enabling Domain Takeover
BSI warns of an unpatched flaw in Windows Server 2025 Active Directory that allows domain takeover via dMSA. Microsoft rates it moderate; Germany rates it ...
1.6 Million Customer Emails Exposed in Etsy and TikTok Shop Data Leak
News
1.6 Million Customer Emails Exposed in Etsy and TikTok Shop Data Leak
An exposed Azure storage bucket leaked 1.6 million customer emails from Etsy, TikTok Shop, and others, revealing names, addresses, and order data.
Everest Ransomware Targets Jordan Kuwait Bank in Alleged Data Breach
News
Everest Ransomware Targets Jordan Kuwait Bank in Alleged Data Breach
Everest ransomware group claims to have breached Jordan Kuwait Bank, stealing 11.7GB of internal data, including personal employee details, and demanding ransom by May 31. ...
Chaos Ransomware Claims Attack on Global Charity Giant Salvation Army
News
Chaos Ransomware Claims Attack on Global Charity Giant Salvation Army
Chaos ransomware has claimed a cyberattack on the Salvation Army, threatening to leak sensitive charity data unless demands are met. Scope and content remain undisclosed. ...
Alleged AT&T Data Breach Exposes 31 Million Records
News
Alleged AT&T Data Breach Exposes 31 Million Records
Hackers claim to have leaked 31 million AT&T user records, including tax IDs and IPs, though researchers cannot confirm the breach due to limited data ...
Russian Espionage Group ‘Laundry Bear’ Hacks Dutch Police and NATO-Aligned Targets
News
Russian Espionage Group ‘Laundry Bear’ Hacks Dutch Police and NATO-Aligned Targets
Dutch intelligence links a new Russian cyber espionage group, Laundry Bear, to attacks on NATO entities and the Dutch police targeting sensitive military and diplomatic ...
Firmware and Bootloaders Under Attack as Hackers Target Pre-OS Environments
News
Firmware and Bootloaders Under Attack as Hackers Target Pre-OS Environments
Hackers are escalating attacks on BIOS and bootloaders, exploiting pre-OS vulnerabilities to maintain persistence, evade detection, and bypass Secure Boot protections.

CVE Vulnerability Alerts
PHP2Shell Attacks on Check Point Gateways Deploy TSGA, ESXi Wiper

Cybersecurity
Maersk Confirms Data Theft as WhiteArmor Demands $5 Million
Cybersecurity
Researchers Unmask Qilin Ransomware Administrator ‘Haise’

TOP CYBERSECURITY HEADLINES

This Week’s Security Spotlight

Cybersecurity
DOJ Seizes $1.2B of North Korea’s Binance Haul, Disrupts FaceStealer
Cybersecurity
Researchers Unmask Qilin Ransomware Administrator ‘Haise’
CVE Vulnerability Alerts
Barracuda Flaws CVE-2026-116606 and CVE-2026-111560 Exploited

CVE Vulnerability Alerts
Intel and AMD Patch Over 200 Vulnerabilities in November Updates

Trending

Daily Briefing Newsletter

Subscribe to the Daily Security Review Email Briefing to stay informed on the latest threats, trends, and technology, along with insightful columns from industry experts.

Featured Videos​

Podcasts

Sorry, we couldn't find any posts. Please try a different search.

  • All
  • AI Security
  • Application Security
  • Blog
  • CVE Vulnerability Alerts
  • Cybersecurity
  • Cybersecurity Newsletter
  • Data Security
  • Endpoint Security
  • Identity and Access Management
  • Information Security
  • Network Security
  • News
  • Phishing
  • Podcasts
  • Product Reviews
  • Ransomware
  • Ransomware Victims
  • Resources
  • Security Spotlight
  • Sponsored
  • Threat Actors
  • Threat Actors
  • Threat Detection Tools
Dell Breach by World Leaks: Extortion Attempt Hits Demo Platform
Dell Technologies is the latest target in a growing trend of data extortion attacks as threat actors pivot away from traditional ransomware. The cybercrime group ...
Termite Ransomware: The Silent Invader
Termite ransomware, active since at least late 2024, targets high-profile organizations. Recent victims include Blue Yonder and Zschimmer & Schwarz, highlighting its broad reach and ...
Ransomware-as-a-Service (RaaS): The Industrialization of Cybercrime and What Enterprises Must Do
Ransomware-as-a-Service (RaaS) enables cybercriminals to launch attacks at scale. Learn how it works, why it’s dangerous, and how enterprises can defend and recover effectively.
Critical VPN Vulnerability: ExpressVPN Exposed IPs via RDP Misrouting
A critical vulnerability in ExpressVPN’s Windows client has put a spotlight on the often-overlooked dangers of debug code making its way into production software. This ...
California Engineer Admits to Stealing U.S. Missile Detection Secrets for China
A California engineer admitted to stealing top-secret U.S. missile tracking technology and funneling it to China, exposing a deep insider espionage operation.
Dior Confirms U.S. Customer Data Compromised in Global Cybersecurity Breach
Dior is alerting U.S. customers about a data breach that exposed personal data. The cyberattack, linked to ShinyHunters, targeted LVMH brands via a third-party vendor. ...
ExpressVPN Flaw Exposed Real IPs During Remote Desktop Sessions on Windows
A bug in ExpressVPN's Windows client leaked real IP addresses during RDP sessions. The issue, now fixed, affected traffic over port 3389 outside the VPN ...
Ring Users Alarmed by Suspicious Device Logins: Amazon Blames Backend Bug, Not Breach
A backend glitch at Ring caused customers to see unknown devices logged into their accounts, but Amazon insists there’s been no security breach or unauthorized ...
Dior Data Breach Exposes U.S. Customer Info in LVMH Vendor Attack
In this episode, we unpack the January 2025 data breach at Dior, the iconic luxury fashion house, which exposed sensitive personal information of U.S. customers—including ...
StrongestLayer Raises $5.2M to Fight AI-Powered Phishing with TRACE
In an era where generative AI is being used not just for productivity but for precision cybercrime, a San Francisco-based startup, StrongestLayer, is taking a ...
750,000 Records Exposed: Inside the TADTS Data Breach by BianLian
In July 2024, The Alcohol & Drug Testing Service (TADTS), a Texas-based company handling sensitive employment-related data, suffered a catastrophic data breach. Nearly 750,000 individuals ...
SS7 Is Still Broken: How Surveillance Firms Are Bypassing Telco Defenses
A new attack technique is exposing just how vulnerable global mobile networks remain in 2025. Cybersecurity firm Enea has discovered a surveillance operation that bypasses ...
Arch Linux Removes Malicious AUR Packages That Deployed Chaos RAT Malware
Arch Linux pulled three AUR packages after discovering they delivered Chaos RAT malware through a malicious GitHub script, compromising Linux systems via community-sourced PKGBUILD files. ...
New CrushFTP Zero-Day Exploit Enables Admin Access on Unpatched Servers
CrushFTP warns of an actively exploited zero-day vulnerability (CVE-2025-54309) allowing full admin access via web interface on unpatched servers running outdated builds.
Widespread Cyberattack Exploits Microsoft SharePoint Zero-Day, Hits U.S. Agencies and Global Targets
Hackers exploited a zero-day in Microsoft SharePoint, breaching U.S. agencies, global businesses, and universities before patches were issued. Some breaches include loss of critical data. ...
Weekly Cybersecurity Newsletter: 14th to 18th August
Explore our latest cybersecurity podcast episodes featuring ransomware attacks, phishing campaigns, corporate breaches, legal showdowns, and deep dives into evolving threats and digital defenses.
BigONE Crypto Exchange Hacked: $27 Million Stolen in Hot Wallet Attack
BigONE cryptocurrency exchange suffered a $27 million breach involving its hot wallet. While user funds are safe, blockchain forensics reveal ongoing laundering of stolen assets. ...
LameHug Malware Uses AI-Powered Language Model to Launch Dynamic Windows Data Theft
LameHug malware uses an AI language model to craft system commands on the fly, targeting Windows machines in attacks linked to Russian-backed APT28.
Louis Vuitton Confirms Multi-Country Data Breaches Linked to Single Cyberattack
Luxury fashion house Louis Vuitton confirmed that recent customer data breaches in the UK, South Korea, and Turkey all trace back to a single cyberattack ...