Cyber Security
DOJ Seizes $1.2B of North Korea’s Binance Haul, Disrupts FaceStealer
TSMC Confirms Employee Data Leak Traced to Third-Party Cloud Vendor
Citrix Patches 28 NetScaler Flaws and Critical Console Auth Bypass
Apify Rotates API Tokens and Urges 2FA Resets After Breach
PostgreSQL Fixes 52 Vulnerabilities and Ends Support for Version 14
PTC Patches Critical Windchill and FlexPLM Flaw CVE-2026-126325
Zoho Publishes Eight Critical ManageEngine CVEs, One Rated 9.9
Mitel Fixes Critical MiVoice MX-ONE Authentication Bypass Flaw
Google Cloud Warns of AMD Turin CPU Flaws Leaking Data in VMs
Red Hat Publishes 21 CVEs, Led by CVSS 9.6 Satellite Sandbox Bypass
School Bomb-Threat Emails Trace to Addresses in Stolen Credential Data
Maersk Confirms Data Theft as WhiteArmor Demands $5 Million
Attackers Hijack ScreenConnect at MSPs as ConnectWise Cuts Extensions
wfx-loot Campaign Used 4,837 Hijacked GitHub Accounts for CI Stealer
Apache 2.4.71 Fixes Critical mod_http2 RCE Flaw CVE-2026-119618
Critical MongoDB Flaw CVE-2026-118383 Crashes Replica Set Members
Node.js Security Releases Fix HTTP/2 Crash and TLS Memory Leaks
Poland Takes ePUAP E-Government Platform Offline After Cyberattack
AntiFox AI Pentest Platform Abused to Steal AWS Production Secrets
Researchers Unmask Qilin Ransomware Administrator ‘Haise’
Critical Red Hat Quay Flaw CVE-2026-123710 Allows Signing Takeover
Zoom Patches Critical Workplace for Windows Flaw CVE-2026-108187
Chrome 157 Update Fixes 83 Flaws, Including Five Critical Bugs
Telegram Patches Android Remote Code Execution Bug After V12 Demo
Public Exploit Released for Linux Kernel AF_UNIX Flaw CVE-2026-80521
Over 35,000 Grok-Built Apps Found Open Online, Some Leaking Data
Microsoft Patches Outlook Zero-Day CVE-2026-124194 in 1,000+ Fixes
SAP Patches Four CVSS 10.0 Flaws Including ICM2SHELL RCE
Xen Orchestra Auth Bypass Exploited to Hijack XCP-ng Hosts
Barracuda Flaws CVE-2026-116606 and CVE-2026-111560 Exploited
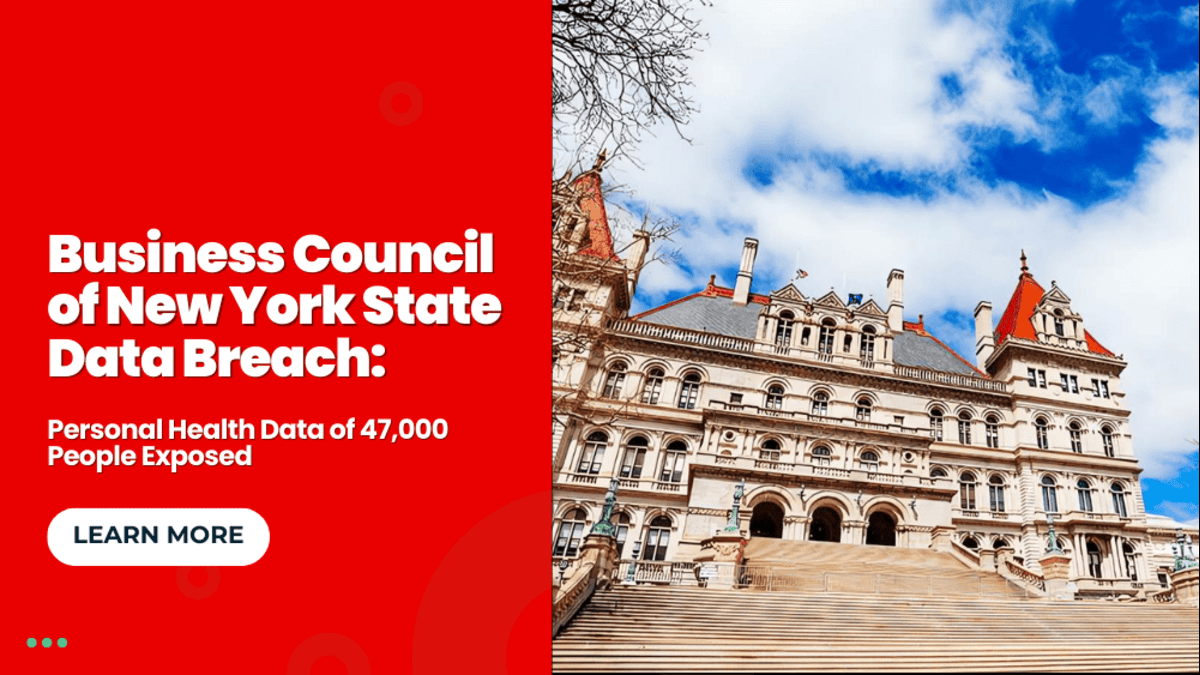
Business Council of New York State Data Breach: Personal Health Data of 47,000 People Exposed
Cybersecurity
Business Council of New York State Data Breach: Personal Health Data of 47,000 People Exposed
BCNYS reports a two-day February intrusion discovered in August exposed personal, financial, and health data for 47,329 people, prompting rolling notifications and credit monitoring for ...
Cybersecurity
Clickjacking Vulnerability Exposes Autofill Data Across Major Extensions
Attackers use ADFS redirect phishing through legitimate office.com links, bypassing URL filters and MFA, to steal Microsoft 365 logins via malvertising and conditional access tricks.
Financial App Data Leak in Turkey Puts Millions at Risk
Cybersecurity
Financial App Data Leak in Turkey Puts Millions at Risk
An unprotected MongoDB tied to FinansCepte and FinansWebde exposed over four million records, putting Turkish users at risk of phishing, credential stuffing, and manipulated financial ...
GenAI Powers Harder-to-Detect Phishing Threats
News
GenAI Powers Harder-to-Detect Phishing Threats
New research from Unit 42 shows adversaries are combining AI website builders, writing assistants, deepfakes, and chatbots to automate large-scale campaigns that closely mimic trusted ...
LG Hai Phong Earns CSMS Level 3 Certification at Its Largest Vehicle Component Base
Cybersecurity
LG Hai Phong Earns CSMS Level 3 Certification at Its Largest Vehicle Component Base
LG’s Hai Phong plant earned CSMS Level 3 Certification from TÜV Rheinland, the first facility to hold both Level 2 and Level 3 simultaneously, validating ...
XenoRAT Malware Campaign Targets Embassies in South Korea
Cybersecurity
XenoRAT Malware Campaign Targets Embassies in South Korea
A multi-stage espionage campaign using XenoRAT malware has targeted foreign embassies in South Korea, with evidence linking the activity to both North Korean and Chinese ...
SentinelOne Expands Partnership With Mimecast to Advance People-Focused Cybersecurity
Cybersecurity
SentinelOne Expands Partnership With Mimecast to Advance People-Focused Cybersecurity
SentinelOne and Mimecast deepen integration, pairing Singularity endpoint telemetry with Human Risk Management to prioritize people-focused cybersecurity and reduce human-caused breaches.
Inotiv Ransomware Attack Disrupts Operations After Qilin Claims 176GB Data Theft
News
Inotiv Ransomware Attack Disrupts Operations After Qilin Claims 176GB Data Theft
Inotiv confirms a ransomware attack encrypted systems and data, disrupting operations. SEC filing cites Qilin claims of 176GB theft as investigators restore and assess impact.
Researcher Harvests 270k Employee Records Exploiting Intel Flaw
Cybersecurity
Researcher Harvests 270k Employee Records Exploiting Intel Flaw
Researcher Eaton Zveare found four flaws that exposed 270,000 Intel employee records via unauthenticated APIs and hardcoded credentials, then received only an automated “Thank You ...
Lexington-Richland 5 Data Breach Exposes Students’ Names, Addresses and SSNs
Cybersecurity
Lexington-Richland 5 Data Breach Exposes Students’ Names, Addresses and SSNs
Lexington-Richland 5 says former students’ names, addresses and Social Security numbers were posted on a threat-actor forum after a June breach; notifications and monitoring offered.
Panera Agrees to $2.5M Settlement After 2024 Data Breach
News
Panera Agrees to $2.5M Settlement After 2024 Data Breach
Panera agrees to a $2.5 million settlement after a February 2024 cyber incident; about 147,321 eligible claimants can seek documented or tiered payments.
IBM Finds “AI Oversight Gap” in Organizations That Suffered AI-Related Breaches
News
IBM Finds “AI Oversight Gap” in Organizations That Suffered AI-Related Breaches
IBM reports 97% of organisations in AI-related breaches lacked AI access controls; shadow AI added $670,000 to average breach costs while defensive AI sped containment.
PayPal Denies Breach Amid 16M Login Leak on Dark Web
News
PayPal Denies Breach Amid 16M Login Leak on Dark Web
A forum post claims 15.8 million PayPal credentials were leaked; PayPal says the data ties to a 2022 incident. Researchers could not verify the full ...
NIST Proposes AI Cybersecurity Overlays to Secure Generative and Predictive Systems
Application Security
NIST Proposes AI Cybersecurity Overlays to Secure Generative and Predictive Systems
The National Institute of Standards and Technology (NIST) has released a concept paper proposing control overlays to secure artificial intelligence (AI) systems, including generative and ...
Microsoft Opens Inquiry After Reports Israel Used Azure For Mass Surveillance
News
Microsoft Opens Inquiry After Reports Israel Used Azure for Mass Surveillance
Microsoft probes allegations Unit 8200 used Azure to store millions of Palestinian call recordings. The company says mass surveillance of civilians would violate Azure terms.
MoD Contractor Data Breach Exposes Thousands Of Afghan Nationals
Cybersecurity
MoD Contractor Data Breach Exposes Thousands Of Afghan Nationals
MoD confirms a contractor-linked data breach affecting up to 3,700 ARAP arrivals, exposing names and passport details and reigniting concerns over subcontractor security and Afghan ...
AT&T Settlement Clears $177M For Victims Of 2019 And 2024 Data Breaches
News
AT&T Settlement Clears $177M for Victims Of 2019 and 2024 Data Breaches
Federal court approves $177 million AT&T settlement covering 2019 and 2024 data breaches; claimants can seek documented losses or tiered payments, with $7,500 maximum possible.
Workday Data Breach Linked To Third-Party CRM Amid Salesforce Social Engineering Wave
Cybersecurity
Workday Data Breach Linked To Third-Party CRM Amid Salesforce Social Engineering Wave
Workday discloses a data breach tied to a third-party CRM after social engineering attacks. No tenant data was accessed; business contact details were exposed amid ...
Healthplex Fined $2M After Phishing-Driven Data Breach Exposed Tens Of Thousands
Cybersecurity
Healthplex Fined $2M After Phishing-Driven Data Breach Exposed Tens Of Thousands
A phishing click at Healthplex exposed tens of thousands’ health data; delayed reporting triggered a $2 million DFS fine and a mandatory independent MFA audit.
Bragg Discloses Cybersecurity Incident; Says Impact Appears Limited
News
Bragg Discloses Cybersecurity Incident; Says Impact Appears Limited
Bragg Gaming Group detected a cybersecurity incident on August 16, 2025. Preliminary findings say the impact was internal only, with no indication personal data was ...

CVE Vulnerability Alerts
PHP2Shell Attacks on Check Point Gateways Deploy TSGA, ESXi Wiper

Cybersecurity
Maersk Confirms Data Theft as WhiteArmor Demands $5 Million
Cybersecurity
Researchers Unmask Qilin Ransomware Administrator ‘Haise’

TOP CYBERSECURITY HEADLINES

This Week’s Security Spotlight

Cybersecurity
DOJ Seizes $1.2B of North Korea’s Binance Haul, Disrupts FaceStealer
Cybersecurity
Researchers Unmask Qilin Ransomware Administrator ‘Haise’
CVE Vulnerability Alerts
Barracuda Flaws CVE-2026-116606 and CVE-2026-111560 Exploited

CVE Vulnerability Alerts
Intel and AMD Patch Over 200 Vulnerabilities in November Updates

Trending

Daily Briefing Newsletter

Subscribe to the Daily Security Review Email Briefing to stay informed on the latest threats, trends, and technology, along with insightful columns from industry experts.

Featured Videos​

  • All
  • AI Security
  • Application Security
  • Blog
  • CVE Vulnerability Alerts
  • Cybersecurity
  • Cybersecurity Newsletter
  • Data Security
  • Endpoint Security
  • Identity and Access Management
  • Information Security
  • Network Security
  • News
  • Phishing
  • Podcasts
  • Product Reviews
  • Ransomware
  • Ransomware Victims
  • Resources
  • Security Spotlight
  • Sponsored
  • Threat Actors
  • Threat Actors
  • Threat Detection Tools
CVE-2025-42957: Active Exploits Target SAP S/4HANA Systems
A newly uncovered critical vulnerability, tracked as CVE-2025-42957, is sending shockwaves through the enterprise technology world. Affecting all SAP S/4HANA deployments, both on-premise and in ...
Fake Job Interviews, Real Hacks: How North Korean Spies Steal Billions in Crypto
North Korean cybercriminals have escalated their social engineering operations, deploying a wave of sophisticated campaigns designed to infiltrate cryptocurrency and decentralized finance (DeFi) organizations. At ...
North Korean Hackers Pose as Recruiters To Launch Global Cyberattacks
North Korean hackers posed as recruiters to target blockchain and finance professionals, exploiting Slack and cyber intelligence platforms to steal cryptocurrency in a global campaign ...
Social Engineering Breach Opens Door to Google Salesforce Data Leak
A phishing attack on a Google employee led to a Salesforce breach, exposing business contact data. Gmail remained secure, but the incident underscores the power ...
Czech Cybersecurity Agency Warns Against Chinese Technology in Critical Infrastructure
The Czech Republic’s cybersecurity agency warns critical infrastructure operators against Chinese technology, elevates threat level to “High,” and cites confirmed malicious activity, data access risks, ...
This Week In Cybersecurity: September 1–5, 2025
News Stories Jaguar Land Rover Cyberattack Severely Disrupts Production Systems Taken Offline Jaguar Land Rover halted operations after a cyberattack disabled its production systems, forcing ...
Cybersecurity Leadership: An Expert Talks Executive Risk
Leah Santos, CISO and Cyber Resilience Advisor Talks Executive Risk
Wealthsimple Data Breach Leaked Client Information Online
Wealthsimple confirmed a September 2025 data breach affecting under one percent of clients. Personal details were exposed, but passwords and funds remained fully secure throughout ...
Hack on In-Flight Connectivity Provider Anuvu Exposes Starlink User Data
Hackers breached inflight connectivity provider Anuvu, exposing sensitive data including Starlink service records, user credentials, and corporate details linked to major airline and maritime customers ...
Chess.com Confirms Data Breach Through Third-Party File Transfer Application
Chess.com disclosed a June 2025 data breach after attackers exploited a third-party file transfer application, exposing personal data of about 4,500 users while leaving main ...
Bridgestone Confirms Cyberattack Disrupts Manufacturing Operations in North America
Bridgestone confirmed a cyberattack disrupting manufacturing at North American plants. The company quickly contained the incident, assured no customer data was compromised, and continues forensic ...
Hackers Turn to HexStrike-AI to Accelerate Exploitation of N-Day Flaws
Hackers are adopting HexStrike-AI, an AI-powered red teaming tool, to exploit Citrix flaws. The automation shrinks patching windows from days to minutes, raising enterprise security ...
Jaguar Land Rover Cyberattack Severely Disrupts Production, Systems Taken Offline
Jaguar Land Rover confirmed a cyberattack that forced factories offline and disrupted production. Systems remain down, though the automaker says no customer data has been ...
GPS Jamming Attack Forces Ursula Von Der Leyen’s Plane to Land Without Navigation
Ursula von der Leyen’s plane was hit by a suspected Russian GPS jamming attack over Bulgaria, forcing pilots to land manually with paper maps after ...
Embassy Breach Alert: Iranian Hackers Exploit 100+ Email Accounts via Phishing
Iranian state-backed hackers have launched a phishing campaign compromising 104 email accounts and targeting 50+ embassies, ministries, and organizations worldwide. Using hijacked government emails and ...
Cato Networks Acquires Aim Security to Bolster AI Defense in SASE
Cato Networks, a leader in Secure Access Service Edge (SASE), has made its first acquisition, purchasing Aim Security, an AI security startup founded in 2022. ...
Tidal Cyber Secures $10M to Advance Threat-Informed Defense
Cybersecurity startup Tidal Cyber, founded in 2022 by three former MITRE experts, has raised $10 million in Series A funding, bringing its total capital to ...
Disney Fined $10M for COPPA Violations Over Mislabeling Kids’ Content on YouTube
Disney has reached a $10 million settlement with the U.S. Federal Trade Commission (FTC) after being found in violation of the Children’s Online Privacy Protection ...
Google Patches 111 Android Flaws in September 2025, Including Two Zero-Days Under Attack
Google has released its September 2025 Android security patches, addressing a staggering 111 unique vulnerabilities, including two actively exploited zero-day flaws that are already being ...
Santa Fe County Website “Hack” Likely Based on Old Source Code
Hackers claimed to leak Santa Fe County’s website source code, but researchers found the data outdated, likely from the early 2010s, raising doubts about its ...