Cyber Security
DOJ Seizes $1.2B of North Korea’s Binance Haul, Disrupts FaceStealer
TSMC Confirms Employee Data Leak Traced to Third-Party Cloud Vendor
Citrix Patches 28 NetScaler Flaws and Critical Console Auth Bypass
Apify Rotates API Tokens and Urges 2FA Resets After Breach
PostgreSQL Fixes 52 Vulnerabilities and Ends Support for Version 14
PTC Patches Critical Windchill and FlexPLM Flaw CVE-2026-126325
Zoho Publishes Eight Critical ManageEngine CVEs, One Rated 9.9
Mitel Fixes Critical MiVoice MX-ONE Authentication Bypass Flaw
Google Cloud Warns of AMD Turin CPU Flaws Leaking Data in VMs
Red Hat Publishes 21 CVEs, Led by CVSS 9.6 Satellite Sandbox Bypass
School Bomb-Threat Emails Trace to Addresses in Stolen Credential Data
Maersk Confirms Data Theft as WhiteArmor Demands $5 Million
Attackers Hijack ScreenConnect at MSPs as ConnectWise Cuts Extensions
wfx-loot Campaign Used 4,837 Hijacked GitHub Accounts for CI Stealer
Apache 2.4.71 Fixes Critical mod_http2 RCE Flaw CVE-2026-119618
Critical MongoDB Flaw CVE-2026-118383 Crashes Replica Set Members
Node.js Security Releases Fix HTTP/2 Crash and TLS Memory Leaks
Poland Takes ePUAP E-Government Platform Offline After Cyberattack
AntiFox AI Pentest Platform Abused to Steal AWS Production Secrets
Researchers Unmask Qilin Ransomware Administrator ‘Haise’
Critical Red Hat Quay Flaw CVE-2026-123710 Allows Signing Takeover
Zoom Patches Critical Workplace for Windows Flaw CVE-2026-108187
Chrome 157 Update Fixes 83 Flaws, Including Five Critical Bugs
Telegram Patches Android Remote Code Execution Bug After V12 Demo
Public Exploit Released for Linux Kernel AF_UNIX Flaw CVE-2026-80521
Over 35,000 Grok-Built Apps Found Open Online, Some Leaking Data
Microsoft Patches Outlook Zero-Day CVE-2026-124194 in 1,000+ Fixes
SAP Patches Four CVSS 10.0 Flaws Including ICM2SHELL RCE
Xen Orchestra Auth Bypass Exploited to Hijack XCP-ng Hosts
Barracuda Flaws CVE-2026-116606 and CVE-2026-111560 Exploited
This Week In Cybersecurity: 23rd June to 27th June
Cybersecurity Newsletter
This Week In Cybersecurity: 23rd June to 27th June
News Stories New ‘FileFix’ Attack Exploits Windows File Explorer to Deliver Stealthy Commands Threat actors use the search-ms URI protocol ...
INC Ransomware: TTPs, Impact and Mitigation
Blog
INC Ransomware: TTPs, Impact and Mitigation
INC Ransomware is a sophisticated threat actor employing advanced techniques for devastating double extortion attacks. This in-depth analysis reveals their methods, targets, and the critical ...
Cyberattack on Hannaford Exposes Data of Over 2.2 Million, Including 95,000 Mainers
News
Cyberattack on Hannaford Exposes Data of Over 2.2 Million, Including 95,000 Mainers
A cyberattack on Hannaford in late 2024 exposed personal data of over 2.2 million people, including 95,000 Mainers, affecting customers and employees alike.
Scattered Spider Expands Attacks to Aviation and Transportation Sectors
News
Scattered Spider Expands Attacks to Aviation and Transportation Sectors
Scattered Spider hackers have shifted their campaign toward aviation and transport, exploiting identity systems and help desks to breach major airlines using sophisticated social engineering. ...
Scattered Spider Ransomware Group Turns Its Focus to North American Airlines
News
Scattered Spider Ransomware Group Turns Its Focus to North American Airlines
Scattered Spider ransomware group is now targeting North American airlines, with Hawaiian Airlines likely the first victim in a wider campaign against aviation and transportation. ...
Data Breaches at Sheffield City Council Surge to Three-Year High Amid Growing Cybersecurity Concerns
News
Data Breaches at Sheffield City Council Surge to Three-Year High Amid Growing Cybersecurity Concerns
Sheffield City Council faced over 1,500 data breaches since 2022, paying £20,000 in claims amid rising human error and cyberattack incidents targeting local governments.
Massive Data Breach Hits U.S. Federal Bureau of Prisons, Exposes Sensitive Inmate Information
News
Massive Data Breach Hits U.S. Federal Bureau of Prisons, Exposes Sensitive Inmate Information
A major data breach allegedly targeting the U.S. Federal Bureau of Prisons has exposed 320GB of sensitive inmate and staff records, prompting a federal investigation. ...
Cross-Border Cyber Fraud Ring Busted After Stealing Over €400,000 Through Compromised Online Seller Accounts
News
Cross-Border Cyber Fraud Ring Busted After Stealing Over €400,000 Through Compromised Online Seller Accounts
Authorities in Germany and Romania dismantled a phishing fraud ring that stole over €400,000 using hijacked online seller accounts and fake listings on a major ...
Hawaiian Airlines Investigates Cybersecurity Event Amid IT Outage, Ransomware Suspected
News
Hawaiian Airlines Investigates Cybersecurity Event Amid IT Outage, Ransomware Suspected
Hawaiian Airlines reports a major cybersecurity event affecting its IT systems. Flights remain operational as authorities investigate a possible ransomware attack targeting the aviation sector. ...
Nth Degree Data Breach Exposes Nearly 40,000 Identities, Including Event Staff and Partners
News
Nth Degree Data Breach Exposes Nearly 40,000 Identities, Including Event Staff and Partners
A data breach at event vendor Nth Degree exposed nearly 40,000 records, including full names and SSNs, raising privacy concerns across high-profile client organizations.
Ahold Delhaize USA Cyberattack Exposes Over 2 Million Individuals in Widespread Data Breach
News
Ahold Delhaize USA Cyberattack Exposes Over 2 Million Individuals in Widespread Data Breach
Ahold Delhaize USA confirms over 2.2 million individuals impacted in a 2024 cyberattack that exposed personal, financial, and medical data from internal company systems.
Why External Attack Surface Management Belongs at the Core of Your Cybersecurity Strategy
Application Security
Why External Attack Surface Management Belongs at the Core of Your Cybersecurity Strategy
Discover why External Attack Surface Management (EASM) is vital for modern digital risk protection and how it enhances visibility, threat detection, and cyber resilience strategies. ...
Pro-Russian Hackers Disrupt Dutch Government Websites Amid Heightened NATO Security
News
Pro-Russian Hackers Disrupt Dutch Government Websites Amid Heightened NATO Security
Pro-Russian hacker group NoName057(16) claims responsibility for a DDoS attack that disrupted Dutch municipal websites during the NATO Summit’s peak security deployment.
OneClik Campaign Exploits Microsoft ClickOnce and AWS to Breach Energy and Industrial Networks
News
OneClik Campaign Exploits Microsoft ClickOnce and AWS to Breach Energy and Industrial Networks
A stealthy malware campaign abuses Microsoft ClickOnce and AWS services to deploy Golang-based RunnerBeacon backdoors targeting energy and industrial organizations with advanced evasion techniques.
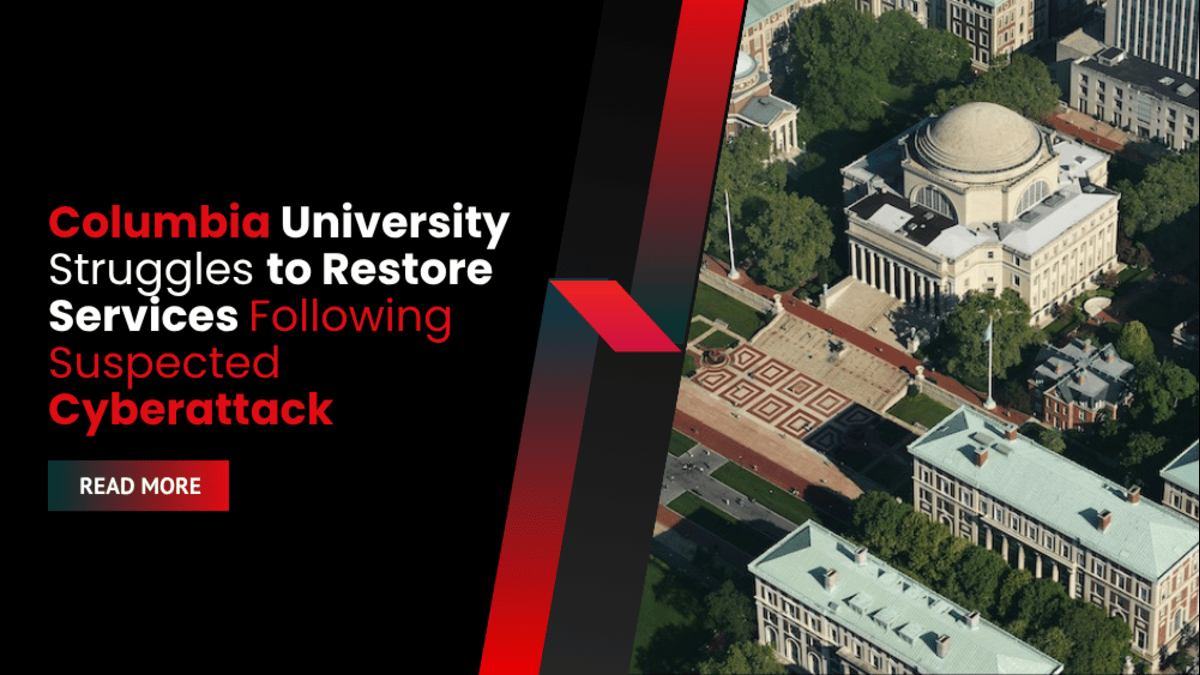
Columbia University Struggles to Restore Services Following Suspected Cyberattack
News
Columbia University Struggles to Restore Services Following Suspected Cyberattack
Columbia University is working to restore critical systems following a suspected cyberattack that has caused widespread outages, impacting thousands of students and faculty.
CISA Confirms Active Exploitation of Critical AMI MegaRAC BMC Vulnerability Enabling Remote Server Hijack
News
CISA Confirms Active Exploitation of Critical AMI MegaRAC BMC Vulnerability Enabling Remote Server Hijack
CISA confirms that a critical vulnerability in AMI MegaRAC BMC firmware is being exploited to hijack servers remotely, prompting urgent patching across government and enterprise ...
Hacker 'IntelBroker' Indicted in $25M Global Data Theft Campaign
News
Hacker ‘IntelBroker’ Indicted in $25M Global Data Theft Campaign
British hacker ‘IntelBroker’ charged by U.S. authorities for stealing and selling sensitive data worldwide, causing $25 million in damage to governments and global enterprises.
French Authorities Arrest BreachForums v2 Operators Behind Global Data Theft Campaigns
News
French Authorities Arrest BreachForums v2 Operators Behind Global Data Theft Campaigns
French police arrest BreachForums v2 operators, including ShinyHunters and IntelBroker, tied to major global and national data breaches affecting millions of users and enterprises.
Scattered Spider: What You Know About It and What You Don’t
Blog
Scattered Spider: The Threat You Think You Know
Scattered Spider isn’t a single group but a sprawling web of identity-based attackers exploiting help desks, MFA gaps, and cloud admin tools to breach enterprises. ...
New FileFix Attack Exploits Windows File Explorer to Deliver Stealthy Commands
News
New FileFix Attack Exploits Windows File Explorer to Deliver Stealthy Commands
A researcher has revealed a new FileFix attack that abuses Windows File Explorer’s address bar to stealthily execute commands, expanding on previous ClickFix phishing techniques. ...

CVE Vulnerability Alerts
PHP2Shell Attacks on Check Point Gateways Deploy TSGA, ESXi Wiper

Cybersecurity
Maersk Confirms Data Theft as WhiteArmor Demands $5 Million
Cybersecurity
Researchers Unmask Qilin Ransomware Administrator ‘Haise’

TOP CYBERSECURITY HEADLINES

This Week’s Security Spotlight

Cybersecurity
DOJ Seizes $1.2B of North Korea’s Binance Haul, Disrupts FaceStealer
Cybersecurity
Researchers Unmask Qilin Ransomware Administrator ‘Haise’
CVE Vulnerability Alerts
Barracuda Flaws CVE-2026-116606 and CVE-2026-111560 Exploited

CVE Vulnerability Alerts
Intel and AMD Patch Over 200 Vulnerabilities in November Updates

Trending

Daily Briefing Newsletter

Subscribe to the Daily Security Review Email Briefing to stay informed on the latest threats, trends, and technology, along with insightful columns from industry experts.

Featured Videos​

Podcasts

Sorry, we couldn't find any posts. Please try a different search.

  • All
  • AI Security
  • Application Security
  • Blog
  • CVE Vulnerability Alerts
  • Cybersecurity
  • Cybersecurity Newsletter
  • Data Security
  • Endpoint Security
  • Identity and Access Management
  • Information Security
  • Network Security
  • News
  • Phishing
  • Podcasts
  • Product Reviews
  • Ransomware
  • Ransomware Victims
  • Resources
  • Security Spotlight
  • Sponsored
  • Threat Actors
  • Threat Actors
  • Threat Detection Tools
ReVault: Critical Dell Firmware Flaws Allow Windows Login Bypass and Persistent Implants
In a powerful reminder that hardware security is just as critical as software defense, Cisco Talos researchers have uncovered “ReVault,” a collection of five high-severity ...
Air France–KLM Data Breach Exposes Customer Info via Compromised Third-Party Platform
The aviation industry has suffered yet another major cybersecurity incident. Air France and KLM have confirmed a data breach impacting customer records via an external ...
Critical Flaws in CyberArk Conjur and HashiCorp Vault Put Enterprise Secrets at Risk
Enterprise secrets managers—long considered the most secure components in modern infrastructure—are now under fire. In a groundbreaking report, cybersecurity firm Cyata revealed 14 critical zero-day ...
Prompt Injection Nightmare: Critical AI Vulnerabilities in ChatGPT, Copilot, Gemini & More
Enterprise AI assistants are revolutionizing productivity—but they’re also opening new doors for cyberattacks. In this episode, we explore explosive research from Zenity Labs, which reveals ...
Air France and KLM Confirm Third-Party Data Breach Impacting Customer Information
Air France and KLM have confirmed a data breach via a third-party vendor, exposing personal information of loyalty members and airline customers to potential cyber ...
Akira Ransomware Disables Microsoft Defender Using Intel Driver Exploit in New Wave of Attacks
Akira ransomware disables Microsoft Defender using Intel’s driver in BYOVD attacks. Researchers warn of new techniques, SonicWall VPN exploits, and trojanized IT tool installers.
MagentaTV Data Leak Exposes Over 324 Million Logs Linked to Deutsche Telekom’s Streaming Platform
A data leak tied to Deutsche Telekom’s MagentaTV platform exposed over 324 million logs, including user IPs, MAC addresses, and session details.
Meta Blocks 6.8 Million WhatsApp Accounts Amid Rising Scam Group Abuse
Meta has blocked 6.8 million WhatsApp accounts tied to scam operations, rolling out new security features to prevent abuse of group invites and direct messaging. ...
Google Confirms Data Breach as Part of Ongoing Salesforce CRM Attacks by ShinyHunters
Google confirms a Salesforce data breach linked to ShinyHunters, who are targeting enterprise CRM systems in a widespread extortion campaign affecting major global brands.
Cisco Reports Data Breach Following Vishing Attack on Employee
Cisco disclosed a data breach impacting Cisco.com user accounts after a vishing attack on an employee, exposing basic user details but no passwords or sensitive ...
Rhysida Ransomware Group Claims Attack on Cookeville Regional Medical Center
Rhysida ransomware gang has claimed the attack on Cookeville Regional Medical Center, threatening to leak sensitive patient and financial data unless the hospital pays a ...
Pandora Confirms Data Breach Linked to Salesforce Credential Theft Campaign
Pandora confirms a data breach linked to Salesforce credential theft campaigns, exposing customer data while attackers continue to target global enterprises through phishing and OAuth ...
PBS Confirms Data Breach After Employee Information Circulates on Discord
PBS confirmed a data breach after corporate contact details for nearly 4,000 employees were leaked and shared on Discord communities, raising concerns over unauthorized exposure ...
New Linux Backdoor “Plague” Evades Detection for Months
A stealthy Linux backdoor named Plague has evaded antivirus detection for months, exploiting PAM authentication modules to provide attackers with persistent SSH access and near-total ...
From Google to LVMH: ShinyHunters’ Salesforce Breaches Spark Global Ransom Crisis
A new wave of cyber extortion is sweeping across global enterprises, and the battlefield is Salesforce CRM. The notorious **ShinyHunters group—tracked internally by Google as ...
Cisco Hit by Vishing Attack: CRM Breach Exposes Millions of User Profiles
Cisco has confirmed a new data breach after a vishing (voice phishing) attack tricked a company representative into exposing access to a third-party CRM system. ...
Ox Security Unveils Agent Ox: AI Tool That Writes Tailored Fixes for Software Vulnerabilities
The world of application security is shifting dramatically as AI begins to move from simply flagging vulnerabilities to actively fixing them. Ox Security has launched ...
Meta Deletes 6.8 Million Scam Accounts as AI-Powered Fraud Rings Exploit WhatsApp
Meta has removed 6.8 million accounts tied to criminal scam centers in the first half of 2025, marking one of the most aggressive crackdowns on ...
APT28 / Fancy Bear: Russian State Sponsored APT
APT28, aka Fancy Bear, a Russian GRU-linked group, conducts sophisticated espionage and information theft campaigns globally, targeting governments and critical infrastructure.
Meta Found Liable: Jury Rules Against Tech Giant in Flo Health Privacy Case
In a landmark decision, a California jury has ruled Meta guilty of violating user privacy laws in a class-action lawsuit tied to the popular Flo ...