Cyber Security
DOJ Seizes $1.2B of North Korea’s Binance Haul, Disrupts FaceStealer
TSMC Confirms Employee Data Leak Traced to Third-Party Cloud Vendor
Citrix Patches 28 NetScaler Flaws and Critical Console Auth Bypass
Apify Rotates API Tokens and Urges 2FA Resets After Breach
PostgreSQL Fixes 52 Vulnerabilities and Ends Support for Version 14
PTC Patches Critical Windchill and FlexPLM Flaw CVE-2026-126325
Zoho Publishes Eight Critical ManageEngine CVEs, One Rated 9.9
Mitel Fixes Critical MiVoice MX-ONE Authentication Bypass Flaw
Google Cloud Warns of AMD Turin CPU Flaws Leaking Data in VMs
Red Hat Publishes 21 CVEs, Led by CVSS 9.6 Satellite Sandbox Bypass
School Bomb-Threat Emails Trace to Addresses in Stolen Credential Data
Maersk Confirms Data Theft as WhiteArmor Demands $5 Million
Attackers Hijack ScreenConnect at MSPs as ConnectWise Cuts Extensions
wfx-loot Campaign Used 4,837 Hijacked GitHub Accounts for CI Stealer
Apache 2.4.71 Fixes Critical mod_http2 RCE Flaw CVE-2026-119618
Critical MongoDB Flaw CVE-2026-118383 Crashes Replica Set Members
Node.js Security Releases Fix HTTP/2 Crash and TLS Memory Leaks
Poland Takes ePUAP E-Government Platform Offline After Cyberattack
AntiFox AI Pentest Platform Abused to Steal AWS Production Secrets
Researchers Unmask Qilin Ransomware Administrator ‘Haise’
Critical Red Hat Quay Flaw CVE-2026-123710 Allows Signing Takeover
Zoom Patches Critical Workplace for Windows Flaw CVE-2026-108187
Chrome 157 Update Fixes 83 Flaws, Including Five Critical Bugs
Telegram Patches Android Remote Code Execution Bug After V12 Demo
Public Exploit Released for Linux Kernel AF_UNIX Flaw CVE-2026-80521
Over 35,000 Grok-Built Apps Found Open Online, Some Leaking Data
Microsoft Patches Outlook Zero-Day CVE-2026-124194 in 1,000+ Fixes
SAP Patches Four CVSS 10.0 Flaws Including ICM2SHELL RCE
Xen Orchestra Auth Bypass Exploited to Hijack XCP-ng Hosts
Barracuda Flaws CVE-2026-116606 and CVE-2026-111560 Exploited
Vulnerability Alert - 30th April, 2025
CVE Vulnerability Alerts
Vulnerability Alert – 30th April, 2025
Staying ahead of emerging cyber threats requires continuous monitoring of newly disclosed vulnerabilities, exploitation trends, and post-compromise behaviors. This page ...
Fighting AI with AI Using Artificial Intelligence to Strengthen Enterprise Cybersecurity
Blog
Fighting AI with AI: Using Artificial Intelligence to Strengthen Enterprise Cybersecurity
The rise of AI-driven cyberattacks necessitates a proactive approach. This blog explores how AI can combat AI cybersecurity threats, highlighting its benefits and risks ...
MTN Ghana Data Breach Impacts 5,700 Customers, Investigation Underway
News
MTN Ghana Data Breach Impacts 5,700 Customers, Investigation Underway
MTN Ghana confirms a data breach affecting 5,700 customers, with investigations ongoing and direct outreach underway to mitigate potential risks and prevent further exposure.
SK Telecom Offers Free SIM Replacements After Malware Breach Impacts USIM Data
News
SK Telecom Offers Free SIM Replacements After Malware Breach Impacts USIM Data
SK Telecom is replacing SIM cards for 25 million users after a malware breach exposed USIM data. Supply limits restrict replacements to 6 million by ...
M&S Cyberattack Halts Online Sales, Triggers Major Financial Impact
News
M&S Cyberattack Halts Online Sales, Triggers Major Financial Impact
Marks & Spencer suspended online orders after a cyberattack over Easter weekend caused major disruptions, wiping £500 million off its stock and impacting daily sales. ...
CISA Flags Broadcom, CommVault, and Active! Mail Vulnerabilities as Actively Exploited
News
CISA Flags Broadcom, CommVault, and Active! Mail Vulnerabilities as Actively Exploited
CISA adds Broadcom, CommVault, and Active! Mail vulnerabilities to KEV catalog following active exploitation reports, urging immediate patching by enterprise and critical infrastructure operators.
27 Million Records Allegedly Leaked from French Retailer Boulanger
Cybersecurity
27 Million Records Allegedly Leaked from French Retailer Boulanger
Personal data linked to over 27 million customer records of French electronics giant Boulanger has been leaked on a public ...
Over 1,200 SAP NetWeaver Servers Exposed to Actively Exploited Critical Vulnerability
News
Over 1,200 SAP NetWeaver Servers Exposed to Actively Exploited Critical Vulnerability
A critical SAP NetWeaver flaw (CVE-2025-31324) is being actively exploited. Over 1,200 servers are exposed, with hundreds already compromised by remote webshell deployments.
VeriSource Confirms Data Breach Impacted 4 Million People After Year-Long Investigation
News
VeriSource Confirms Data Breach Impacted 4 Million People After Year-Long Investigation
Marks & Spencer Cyberattack Tied to Scattered Spider Ransomware Group
News
Marks & Spencer Cyberattack Tied to Scattered Spider Ransomware Group
Marks & Spencer is battling an ongoing outage caused by Scattered Spider ransomware attackers, who breached its systems, stole password data, and encrypted virtual machines. ...
Darcula: AI-Enhanced Phishing Platform Targets Users Worldwide
News
Darcula: AI-Enhanced Phishing Platform Targets Users Worldwide
The Darcula phishing platform has been upgraded with AI, enabling cybercriminals to quickly generate multilingual phishing scams and harvest user credentials on a global scale. ...
Major AI Vulnerability Exposed: Single Prompt Grants Full Control
News
Major AI Vulnerability Exposed: Single Prompt Grants Full Control
Researchers uncovered a major AI vulnerability allowing attackers to bypass safeguards with a single prompt, gaining control over AI systems to generate dangerous content.
13 Cybersecurity Assumptions That Are Getting You Hacked (And What to Do Instead)
Cybersecurity
13 Cybersecurity Assumptions That Are Getting You Hacked (And What to Do Instead)
Cybersecurity myths are more dangerous than you think. Here are 13 common myths that are silently sabotaging your security—and what to do instead.
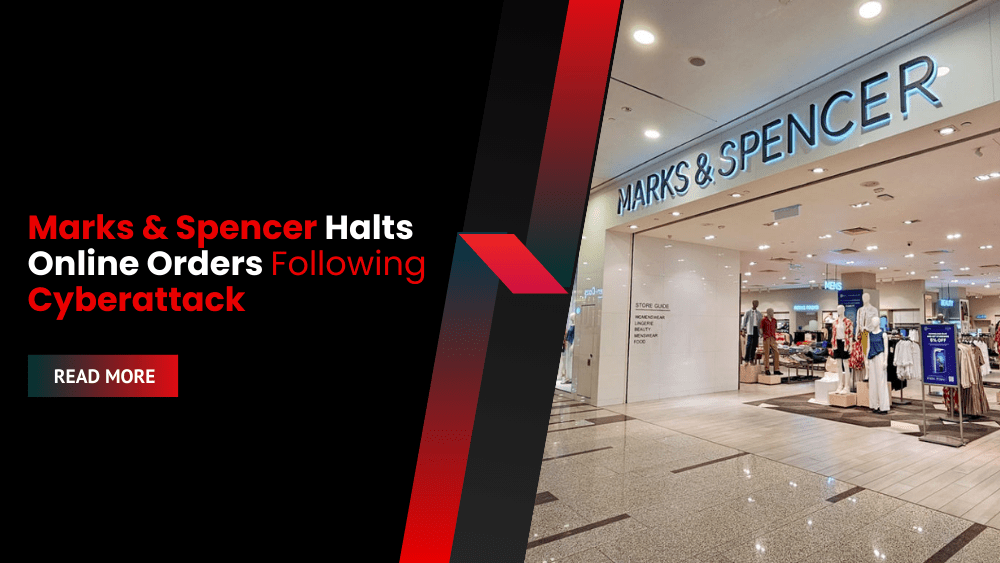
Marks & Spencer Halts Online Orders Following Cyberattack
News
Marks & Spencer Halts Online Orders Following Cyberattack
Marks & Spencer suspended online orders following a cyberattack impacting digital and in-store services, while investigations continue in collaboration with external cybersecurity specialists.
WooCommerce Admins Targeted by Fake Security Patches Delivering WordPress Backdoors
News
WooCommerce Admins Targeted by Fake Security Patches Delivering WordPress Backdoors
A new phishing campaign is targeting WooCommerce administrators with fake security alerts designed to hijack websites by installing hidden backdoors and persistent malware.
Pro-Russian Hackers NoName Intensify DDoS Attacks Against German Organizations
News
Pro-Russian Hackers NoName Intensify DDoS Attacks Against German Organizations
Pro-Russian hackers NoName057(16) have intensified DDoS attacks against German organizations, targeting banks, manufacturers, and government websites in retaliation for political decisions related to Ukraine.
DragonForce Expands Ransomware Model with White-Label Branding
News
DragonForce Expands Ransomware Model with White-Label Branding
DragonForce expands its ransomware cartel with a white-label model, allowing affiliates to use its infrastructure under their own brand, taking a 20% cut of ransoms. ...
SK Telecom Shares Drop Sharply Following a Cyberattack and Customer Data Breach
News
SK Telecom Shares Drop Sharply Following a Cyberattack and Customer Data Breach
SK Telecom Reports Customer Data Breach Linked to Cyberattack SK Telecom, South Korea’s largest mobile carrier, announced that it suffered ...
Navigating the Complex Intersection of AI and Data Privacy
Blog
Navigating the Complex Intersection of AI and Data Privacy
The rise of artificial intelligence (AI) presents incredible opportunities, but it also introduces complex challenges regarding data privacy. This blog post delves into the crucial ...
Russian Military Targeted by AlpineQuest Android Spyware Hidden in Trojanized Mapping App
News
Russian Military Targeted by AlpineQuest Android Spyware Hidden in Trojanized Mapping App
Spyware hidden in a fake AlpineQuest app is stealing sensitive data from Russian soldiers, revealing operational plans via location tracking and real-time Telegram monitoring.

CVE Vulnerability Alerts
PHP2Shell Attacks on Check Point Gateways Deploy TSGA, ESXi Wiper

Cybersecurity
Maersk Confirms Data Theft as WhiteArmor Demands $5 Million
Cybersecurity
Researchers Unmask Qilin Ransomware Administrator ‘Haise’

TOP CYBERSECURITY HEADLINES

This Week’s Security Spotlight

Cybersecurity
DOJ Seizes $1.2B of North Korea’s Binance Haul, Disrupts FaceStealer
Cybersecurity
Researchers Unmask Qilin Ransomware Administrator ‘Haise’
CVE Vulnerability Alerts
Barracuda Flaws CVE-2026-116606 and CVE-2026-111560 Exploited

CVE Vulnerability Alerts
Intel and AMD Patch Over 200 Vulnerabilities in November Updates

Trending

Daily Briefing Newsletter

Subscribe to the Daily Security Review Email Briefing to stay informed on the latest threats, trends, and technology, along with insightful columns from industry experts.

Featured Videos​

Podcasts

Sorry, we couldn't find any posts. Please try a different search.

  • All
  • AI Security
  • Application Security
  • Blog
  • CVE Vulnerability Alerts
  • Cybersecurity
  • Cybersecurity Newsletter
  • Data Security
  • Endpoint Security
  • Identity and Access Management
  • Information Security
  • Network Security
  • News
  • Phishing
  • Podcasts
  • Product Reviews
  • Ransomware
  • Ransomware Victims
  • Resources
  • Security Spotlight
  • Sponsored
  • Threat Actors
  • Threat Actors
  • Threat Detection Tools
Sophisticated Cyberattack on the International Criminal Court: Justice in the Crosshairs
The International Criminal Court (ICC), the world’s foremost tribunal for prosecuting war crimes, genocide, and crimes against humanity, has confirmed yet another sophisticated cyberattack, highlighting ...
Qantas Data Breach: Third-Party Hack Exposes Millions of Frequent Flyers
In a stark reminder of the aviation industry’s growing exposure to cyber threats, Australian airline Qantas recently confirmed a serious data breach—this time not from ...
International Criminal Court Investigates Another Sophisticated Cyberattack
The International Criminal Court confirms a second cyberattack in two years, citing a sophisticated breach and ongoing threats targeting its global judicial infrastructure.
Aeza Group Sanctioned by U.S. Treasury for Enabling Cybercriminal Infrastructure
The U.S. Treasury sanctioned Aeza Group for hosting ransomware and malware infrastructure used by threat groups like BianLian, RedLine, and darknet marketplace BlackSprut.
Berlin Regulator Targets DeepSeek AI Over Data Transfers to China
Germany’s battle over digital sovereignty and data privacy has intensified, with the Berlin Commissioner for Data Protection formally requesting that Google and Apple remove the ...
CISA Flags Citrix NetScaler Flaws: What CVE-2025-6543 Means for Federal and Private Networks
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added multiple Citrix NetScaler vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog—an urgent signal for federal ...
Cato Networks Secures $359M to Fuel AI-Powered SASE Expansion
Cato Networks just raised $359 million in Series G funding, pushing its valuation past $4.8 billion and its total funding beyond the $1 billion mark—a ...
Europol Busts $540 Million Crypto Fraud Ring Operating Across Multiple Countries
Europol dismantles a $540 million crypto investment fraud ring targeting thousands across borders. The syndicate used AI tools, shell companies, and crypto wallets for laundering. ...
FBI Issues Alert as Cybercriminals Impersonate Health Fraud Investigators to Steal Patient Data
FBI warns of cybercriminals impersonating health fraud investigators to steal sensitive medical data. Fraudulent emails and texts are targeting patients and providers nationwide.
Johnson Controls Begins Notifying Individuals Impacted by 2023 Ransomware Attack
Johnson Controls is notifying individuals impacted by a 2023 ransomware attack that exposed data and disrupted global operations. Dark Angels ransomware group is believed responsible. ...
Ransomware Attack on Swiss Government Vendor Leads to Massive Data Leak
Switzerland confirms government data was stolen in a ransomware attack on Radix. Leaked records include documents, contracts, and communications now circulating on the dark web. ...
Europol Busts $540 Million Crypto Fraud Ring Operating Across Multiple Countries
Europol dismantles a $540 million crypto investment fraud ring targeting thousands across borders. The syndicate used AI tools, shell companies, and crypto wallets for laundering. ...
Canada Orders Hikvision to Shut Down National Operations Over Security Concerns
Canada orders Hikvision to shut down operations after a national security review. Government bans all public sector use of Hikvision surveillance equipment nationwide.
Chrome’s Latest Zero-Day: CVE-2025-6554 and Remote Code Execution Risks
A new high-severity zero-day vulnerability in Google Chrome—CVE-2025-6554—has sent shockwaves across the cybersecurity landscape. This episode dives into the technical details, real-world impact, and broader ...
Russia’s 16KB Curtain: Cloudflare Throttling and the Future of the RuNet
Russia has entered a new phase of digital authoritarianism. In a sweeping move, Russian Internet Service Providers (ISPs) have begun systematically throttling access to Cloudflare ...
Ahold Delhaize Data Breach: 2.2 Million Employee Records Exposed
Ahold Delhaize, one of the world’s largest food retailers, is now the subject of one of the most significant ransomware breaches in recent U.S. history. ...
This Week In Cybersecurity: 23rd June to 27th June
News Stories New ‘FileFix’ Attack Exploits Windows File Explorer to Deliver Stealthy Commands Threat actors use the search-ms URI protocol in Windows File Explorer to ...
Why Canada Banned Hikvision: National Security vs. Geopolitics
Canada has taken a definitive stance in the escalating global scrutiny of Chinese technology, ordering surveillance giant Hikvision to cease all operations within its borders. ...
INC Ransomware: TTPs, Impact and Mitigation
INC Ransomware is a sophisticated threat actor employing advanced techniques for devastating double extortion attacks. This in-depth analysis reveals their methods, targets, and the critical ...
Scattered Spider Takes Flight: Inside the Cybercrime Group’s Move into Aviation
As the aviation industry becomes more digitally interconnected, its exposure to sophisticated cyber threats continues to grow. One of the most dangerous actors in this ...